
Customer Snapshot
| Attribute | Details |
|---|---|
| Industry | FinTech / SaaS |
| Cloud Environment | GCP (70%), Azure (30%) |
| Workloads | GKE + VMs; two enterprise products on GCP |
| Databases | MySQL (primary OLTP), plus a document store |
| Sensitive Data | Customer and transaction data in production MySQL tables |
| DB Access | 10–15 people with some form of database access |
| Compliance | ISO 27001, SOC 1, SOC 2, GDPR |
| Current State | No query-level audit, no masking, broad/shared DB access |
| Focus Area | Data-tier governance for MySQL |
The Situation: The Application Tier Is Governed, the Data Tier Isn’t
This FinTech runs two enterprise SaaS products on GCP, both processing financial transactions through an OLTP data tier built on MySQL. The team had done real work on posture and infrastructure — multi-cloud visibility, workload security, access controls at the cloud and cluster layer were all moving in the right direction. But behind the application services sat the MySQL databases holding customer and transaction data, and the data tier had none of the same rigor applied to it.
The uncomfortable questions were the ones nobody could answer confidently. Who queried the customer tables last week, and what did they pull? Can a support engineer run SELECT * and export every record? If a GDPR assessor or an ISO 27001 auditor asked for query-level access logs on the tables holding personal and financial data, was there anything to hand over? The honest answers were “we don’t know,” “yes,” and “no.” The application tier was watched. The data — the thing regulations, auditors, and customers actually care about — was effectively open behind it.
The Core Tension
Access control gets someone into the database; it does nothing about what they can see and do once inside. Native MySQL privileges and grants are too coarse to mask a column, block a dangerous statement, or record who ran what at the query level. So even a reasonable access model leaves a gap: a legitimately-connected engineer can read every customer’s data in plaintext and export it, with no record and no restraint. Closing that gap requires a control layer at the query itself — one that governs and records every statement without shipping sensitive financial data out of the team’s own GCP environment to a third-party vendor.
Where the Gaps Were
No Record of Who Queried What
MySQL’s native logging, where enabled at all, typically shows that a connection happened under a shared or service account — not which human ran which statement, against which tables, returning how many rows. When the question is “who accessed customer data and what did they retrieve,” connection-level logging is not an answer. The forensic detail that matters — the statement, the human, the tables, the volume — is simply not captured. For a FinTech, that is both an operational blind spot and a direct audit liability.
Everyone Sees Raw Data
Without masking, any user who can read a table sees every column in plaintext. A support engineer investigating one customer’s issue can see every customer’s personal and financial details. There is no role-based distinction between “needs to see this one customer’s account status” and “can read all sensitive fields for everyone.” Under GDPR, where access to personal data is supposed to be limited to a legitimate, scoped business need, this blanket visibility is exactly what an assessor looks for and does not want to find.
No Guardrail Against Destructive or Bulk Operations
A mistyped DELETE without a WHERE clause, a DROP TABLE during what was meant to be a read-only debugging session, or a SELECT * that pulls a million rows — native access has no safety net. The statement reaches MySQL and executes. For an OLTP system processing live financial transactions, a destructive query against production is not a hypothetical; it is an incident waiting for a bad afternoon. Prevention — stopping the dangerous statement before it runs — does not exist in the default setup.
The Data-Sovereignty Trap
The obvious fix — a legacy database activity monitoring product — often carries its own problem: routing sensitive query traffic and results through the vendor’s infrastructure. For a FinTech that cares about where its customer and transaction data lives, and that operates under GDPR and ISO 27001, shipping every query and every result set through a third party is a non-starter. The team needed monitoring and control without surrendering data sovereignty.
How Cloudanix Addresses This Situation
A Secure Query Proxy in Your Own Cloud
Cloudanix Database Activity Monitoring deploys as a secure query proxy that runs inside the customer’s own environment. Every SQL statement to the MySQL databases routes through the proxy, and every audit record lands in the customer’s own storage. The database stays in its private subnet; the sensitive data never leaves the team’s own GCP account to be secured. This is the direct answer to the data-sovereignty trap: full query-level control and monitoring, with nothing shipped to a vendor.
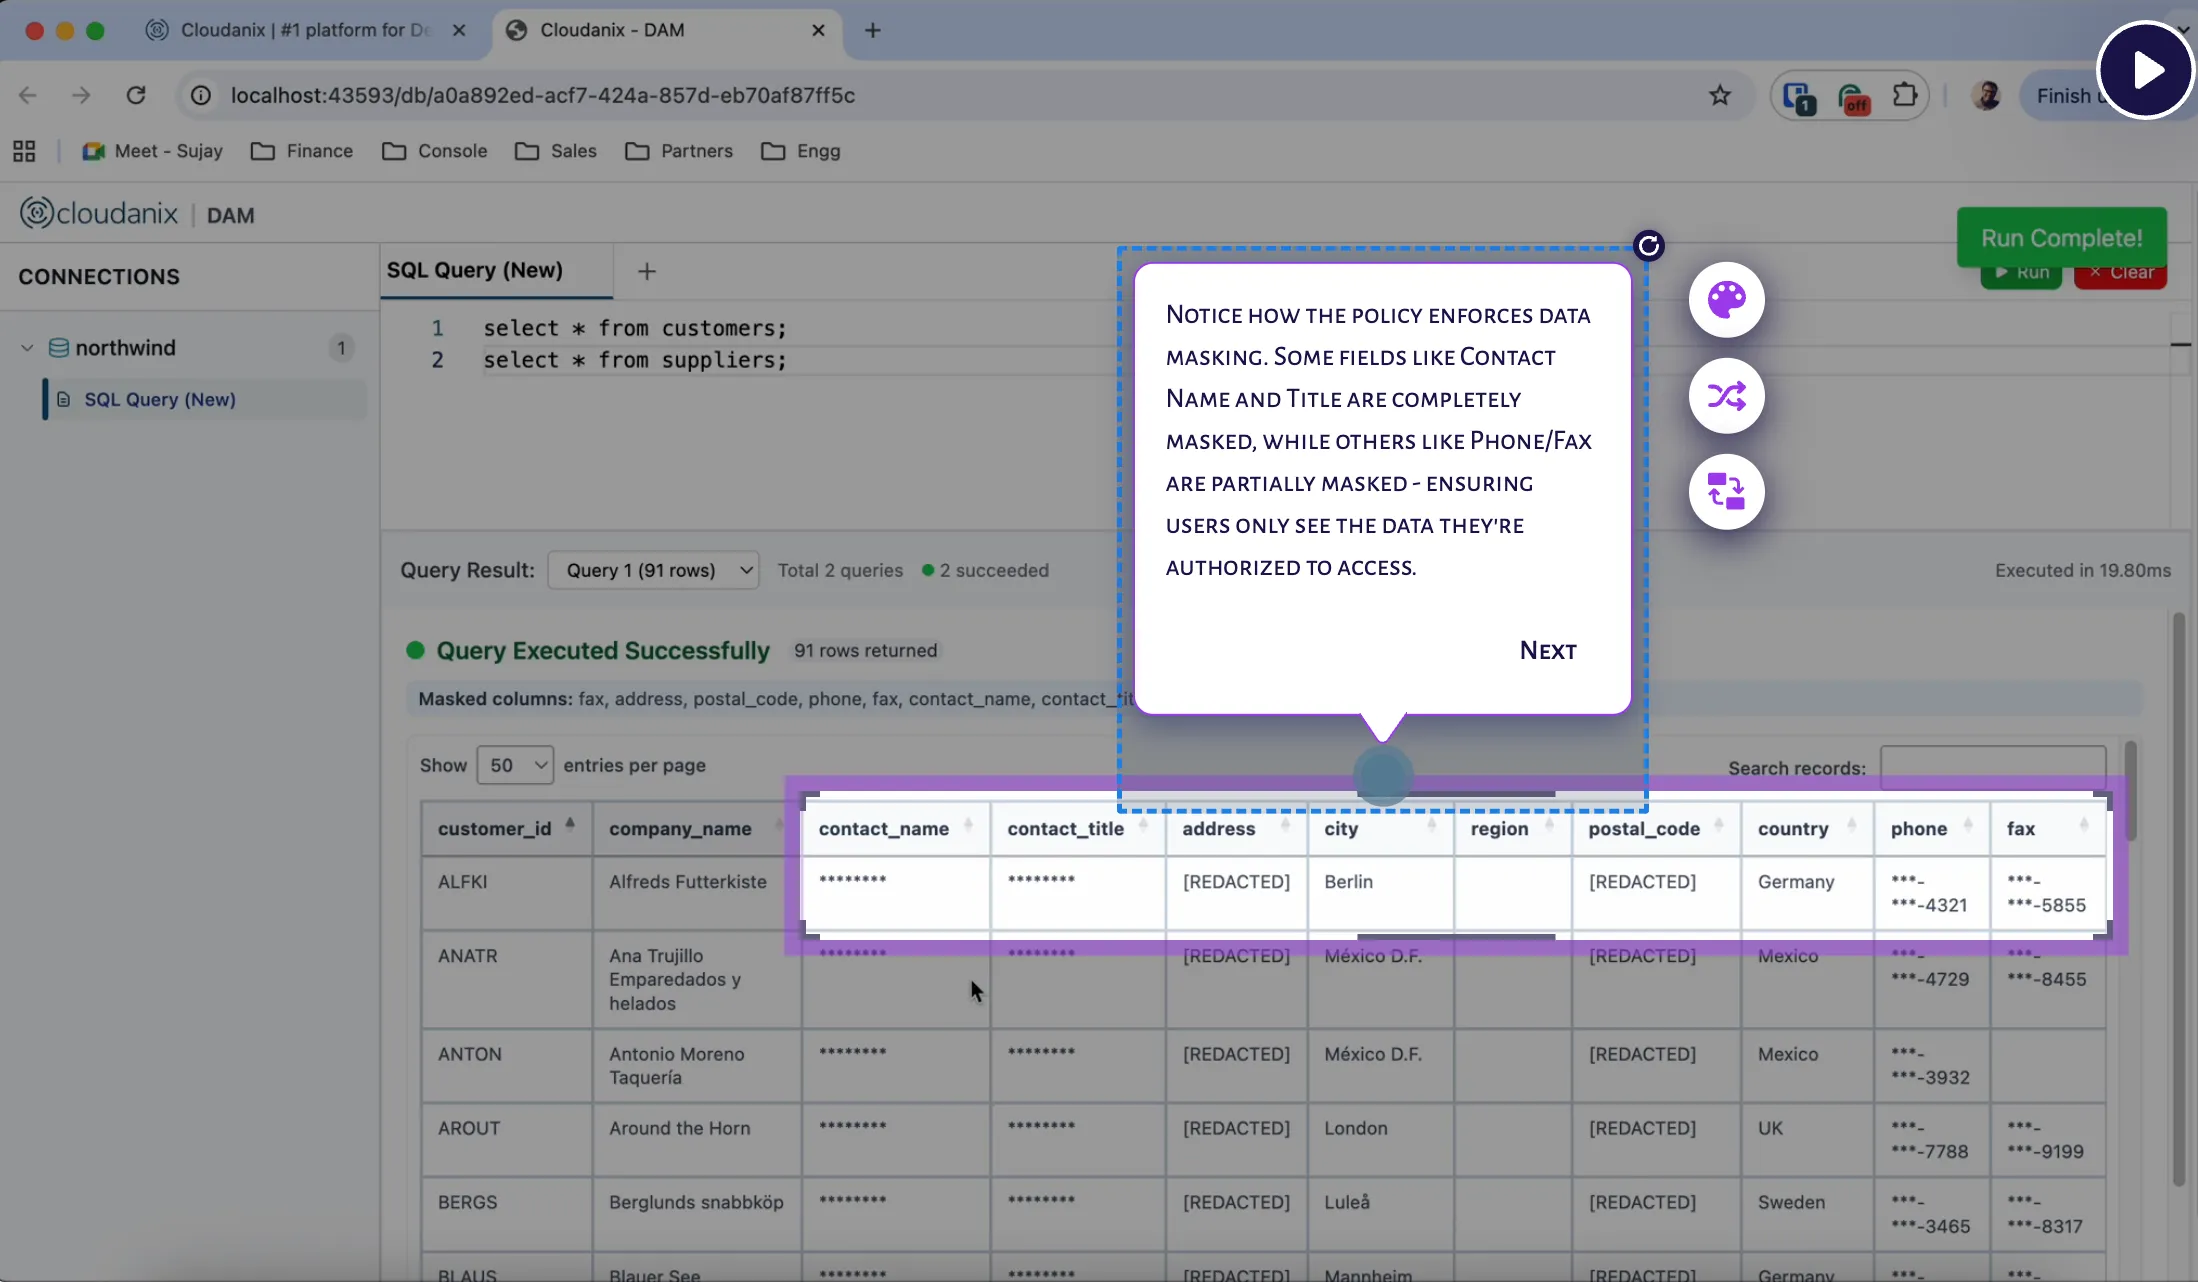
Query-Level Audit: Every Statement, Every Human
DAM logs every query with full context — the statement itself, the identity of the real human who ran it, the tables and columns touched, rows returned, and timing. Even where MySQL sees a shared connection, the query is attributed to the actual person. The previously unanswerable question — “who queried the customer tables and what did they pull?” — becomes a search against the audit trail in the team’s own storage. For an auditor’s “show me who accessed personal data in the last quarter,” the answer is one query, not weeks of reconstruction.
Dynamic, Role-Based Masking
DAM applies real-time data masking post-execution based on who is asking, with multiple strategies — full mask, show last four, mask email or phone, hash, redact, tokenize. A support engineer sees a customer’s status and a masked identifier; a role with a genuine need sees more. Masking happens at the query layer, so there are no schema changes and no application changes. The same query returns different visibility depending on the requester’s role. This is the mechanism that lets the team honour GDPR’s data-minimisation principle in practice rather than on paper.
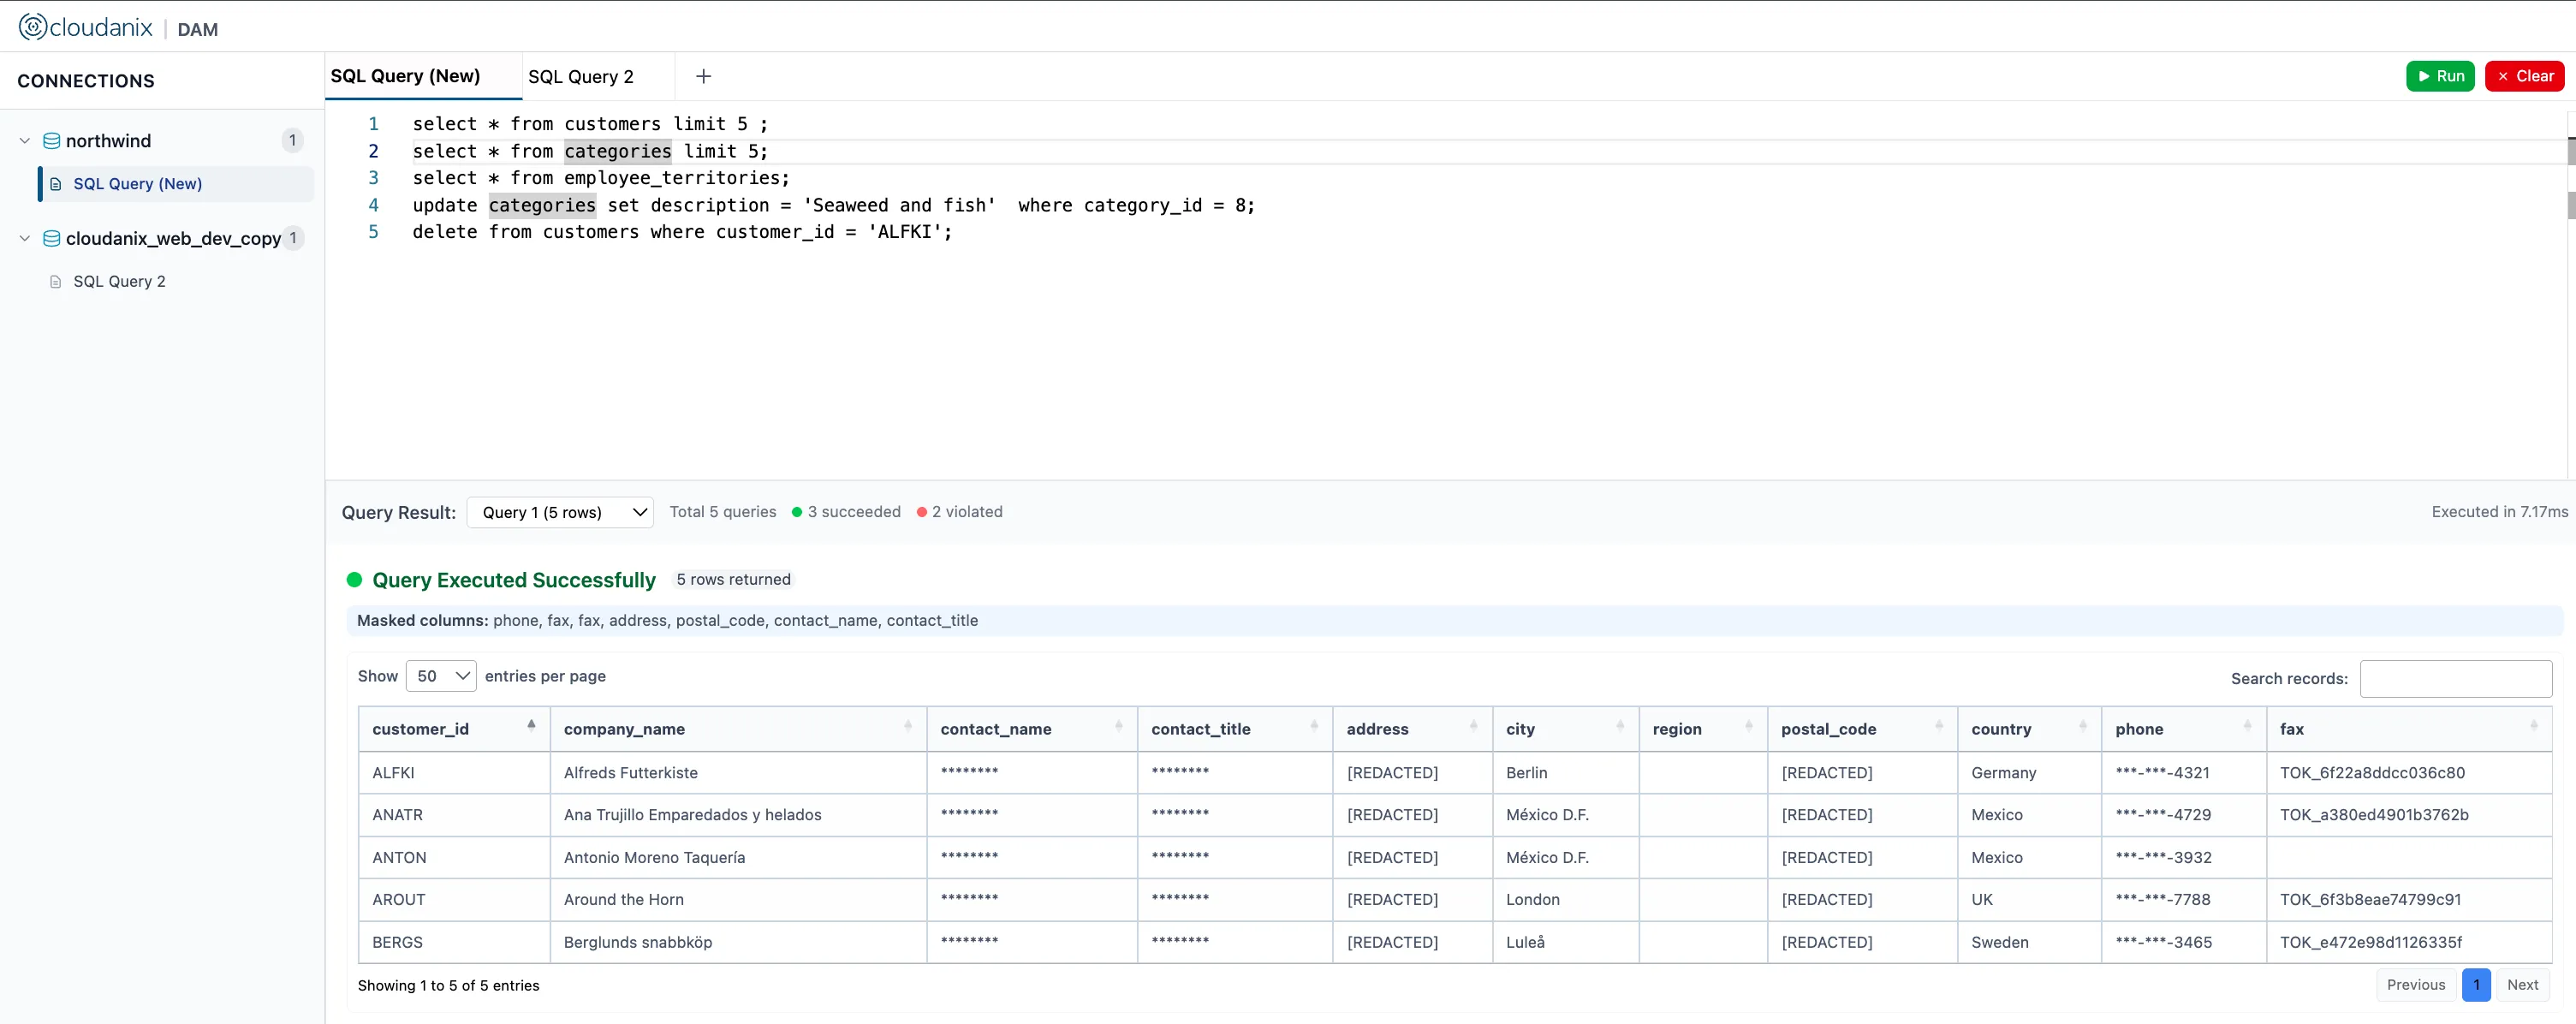
Guardrails: Blocking Dangerous Queries Before Execution
DAM inspects statements before they run and enforces guardrails: block destructive operations such as DELETE, DROP, and TRUNCATE per policy; require a WHERE clause; restrict access to specific tables or columns; and cap row counts to prevent mass export. It also sanity-checks statements for injection patterns and tautologies before execution. A blocked query returns a clear message explaining why. The safety net lives at the query layer — the statement that would have deleted production transaction data or exported a million customer rows never reaches MySQL.
Works With the Tools Engineers Already Use
Because DAM presents a standard database endpoint, engineers keep using MySQL Workbench, DBeaver, DataGrip, TablePlus, or the mysql CLI. There is no browser-based SQL console to adopt and no workflow to relearn. The only change is that access is governed, masked, and recorded — invisibly, from the engineer’s point of view.
The Foundation: Keyless, Identity-Stamped Access
DAM builds on Database JIT: access is requested, approved, and time-bound, with short-lived credentials minted per session instead of shared passwords living on laptops. That is what makes query attribution to a real human possible in the first place — access control and data control working as one lifecycle rather than two bolted-together products. For this team, it also means no MySQL credential ever persists on an engineer’s machine, so a lost laptop carries no database access with it.
See Cloudanix DAM in Action
In this 2-minute interactive walkthrough, see how Cloudanix DAM inspects, masks, and records queries — with your data never leaving your cloud.
Platform Impact
| Dimension | Before | After (DAM on MySQL) |
|---|---|---|
| Query attribution | Connection under shared account | Every statement stamped to the real human |
| Data visibility | Raw plaintext for anyone who can read | Role-based masking at the query layer |
| Destructive/bulk queries | Execute with no safety net | Blocked before execution per policy |
| Audit evidence | Little to none | Full query-level trail in your own storage |
| Data sovereignty | At risk with vendor-routed tools | Proxy in your cloud; data never leaves |
| Credential exposure | Shared passwords on laptops | Short-lived, per-session, nothing persists |
| Engineer workflow | — | Unchanged — same MySQL clients |
Why This Matters More for an OLTP FinTech
An OLTP database for a FinTech is not a reporting warehouse that can tolerate loose access. It is the live system of record for financial transactions and customer data, queried daily by engineers debugging real issues under real time pressure. That combination — high sensitivity, high query volume, high urgency — is exactly where the gap between “has access” and “should see everything” does the most damage. A well-governed application tier makes the ungoverned data tier more glaring, not less, because the data tier is the one layer holding what GDPR, ISO 27001, SOC 2, and the company’s own customers actually care about.
Closing that gap does not mean surrendering the data to a monitoring vendor. A query proxy in the team’s own GCP environment gives the whole picture — who ran what, masked by role, with dangerous statements stopped before they execute — while the sensitive data stays exactly where it belongs. For a MySQL-backed FinTech, that is how the data tier finally earns the same rigor the rest of the stack already has. (For the fundamentals, see what Database Activity Monitoring is.)
Access Without Data Control Is Half a Solution
Getting someone safely into a database means very little if, once inside, they can read and export every customer record unmasked and unlogged. Database JIT answers “who can get in, for how long, and with whose identity.” DAM answers “what can they see, what can they do, and what did they actually do” — masking by role, blocking destructive statements before they run, and recording every query to a named human. Together they are one lifecycle: access control and data control, not two separate products stitched together after the fact. For a FinTech whose business is financial data, that combined control is not overhead — it is the baseline the data tier has been missing.
Key Outcomes
- ✅ Query-Level Audit: Every statement attributed to the real human, in your own storage.
- ✅ Role-Based PII Masking: Sensitive columns masked by who is asking — no schema changes.
- ✅ Query Guardrails: Destructive and bulk operations blocked before execution.
- ✅ Data Sovereignty: Proxy runs in your cloud; data never leaves your account.
- ✅ Native Tooling: MySQL Workbench, DBeaver, DataGrip, TablePlus, mysql CLI — unchanged.
- ✅ Access + Data as One: Built on keyless, identity-stamped Database JIT.
- ✅ Audit-Ready for GDPR & ISO 27001: Who accessed personal data, masked by role, provable on demand.
Sensitive Data in MySQL Behind Your Application Services?
If your MySQL OLTP databases hold customer and transaction data — and you can’t prove who queried what or stop a full-table export — Cloudanix DAM adds query-level audit, role-based masking, and prevention, with your data never leaving your own cloud.
Book a Free Assessment to see DAM protecting your MySQL databases in under 30 minutes.
Related Resources
- Query-Level Audit and PII Masking for RDS Databases Behind ECS Workloads
- The End of Permanent Access: Just-In-Time Granular Database Security
- Database Activity Monitoring: Real-Time Data Security
- What is Real-Time Data Masking?
- Database Activity Monitoring Use Cases: How DAM Prevents Data Loss
- JIT Access and Database Activity Monitoring for a Lean RBI-Regulated FinTech
- What is DPDPA Compliance?













