
Cloudanix Achieves AWS Security Competency Status for Its CNAPP+ Platform and Just-in-Time Access Engine

Cloudanix – Your Partner in Cloud Security Excellence

Richer Vulnerability Data in Bitbucket Merge Requests With PR Quality Gates

  • Sunday, Oct 25, 2026

Customer Snapshot

AttributeDetails
IndustryGig-economy / Workforce SaaS Platform
Cloud EnvironmentAWS
Code & CIBitbucket for SCM, Jenkins for CI
Team StructureLean DevOps team supporting ~20 engineers
Focus AreaActionable security signal at the merge request

The Situation: The Merge Request Said “There’s a Problem” — But Not Enough to Fix It

This team wanted their security signal to land at the merge request — the moment a change is under review and the developer is still in context. They had code security reporting into Bitbucket merge requests, but the feedback shared there was, in the tech lead’s words, just high-level details. The merge request would indicate that a vulnerability scan had run and that something was flagged, without the specifics a developer needs to actually resolve it: which dependency, which version, which line, what the fix is.

High-level signal at the MR is better than nothing, but it creates a frustrating handoff. The developer sees “vulnerabilities found,” then has to leave the review, open a separate dashboard, hunt for the finding, and reconstruct the context the MR should have carried in the first place. For a lean team, that friction is exactly what causes security feedback to be deferred rather than acted on.

The Core Tension

Security feedback is only useful at the point where it can be acted on cheaply — during review, before merge. But feedback that arrives at that point without enough detail to act fails anyway: it tells the developer there is a problem without telling them what to do, which converts the merge request from a decision point into a pointer to go look elsewhere. The value is in detail and placement together.

Where the Gaps Were

Signal Without Specifics

“This MR has vulnerabilities” is a status, not a finding. Without the dependency name and version, the file and line, the severity with its reasoning, and a remediation path, the developer cannot close the loop inside the review. The MR becomes a notification rather than a workspace.

Context Lost in the Handoff to a Dashboard

Every time a developer has to leave the merge request to find detail elsewhere, context is lost and momentum stalls. The review tab and the security dashboard are two different mental spaces, and the switch between them is where findings go to wait.

No Enforcement Tied to the Signal

A high-level note in the MR with no gate behind it is advisory only. There is nothing stopping a genuinely risky change from merging, because the signal does not connect to a pass/fail decision.

How Cloudanix Addresses This

Detailed Findings Posted at the Merge Request

Cloudanix Code Security connects to Bitbucket and auto-scans pull/merge requests, posting a comment and status check with the detail developers need: the specific SAST or SCA finding, where it is in the code, the severity and why, and remediation guidance — not just a “something was found” summary. The review and the fix context live in the same place.
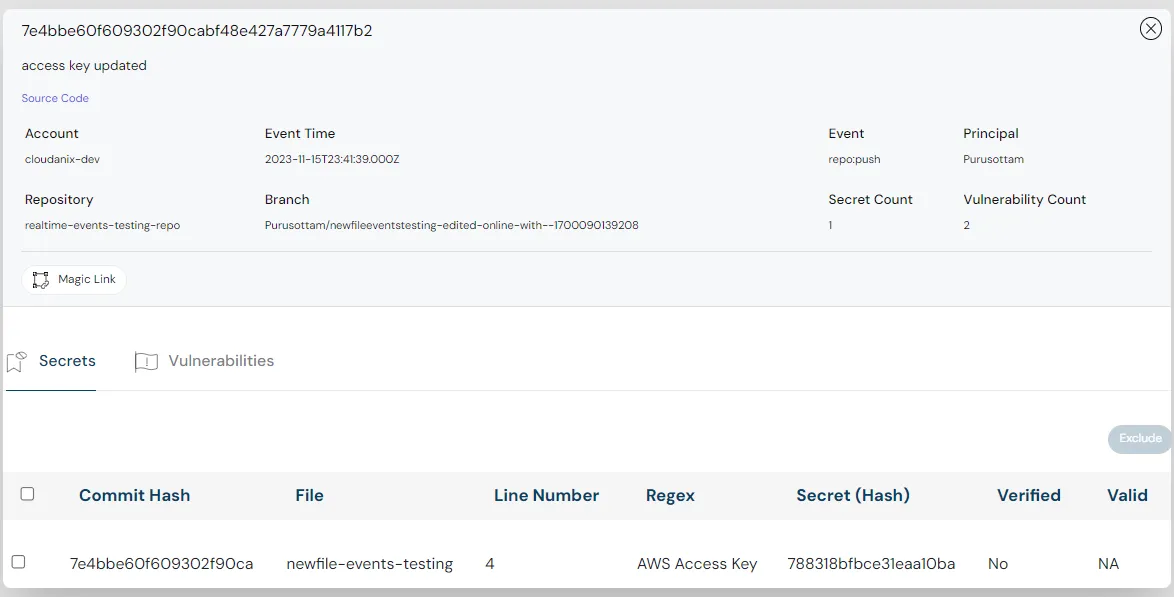
Cloudanix Code Security — Pull request scanning with detailed findings

A Configurable Quality Gate That Can Block the Merge

Beyond annotation, Cloudanix supports quality gates at tenant and repository level that can fail the merge request on findings above a chosen threshold. The signal stops being advisory and becomes an enforced checkpoint — a genuinely risky change cannot merge until it is addressed or explicitly excepted.
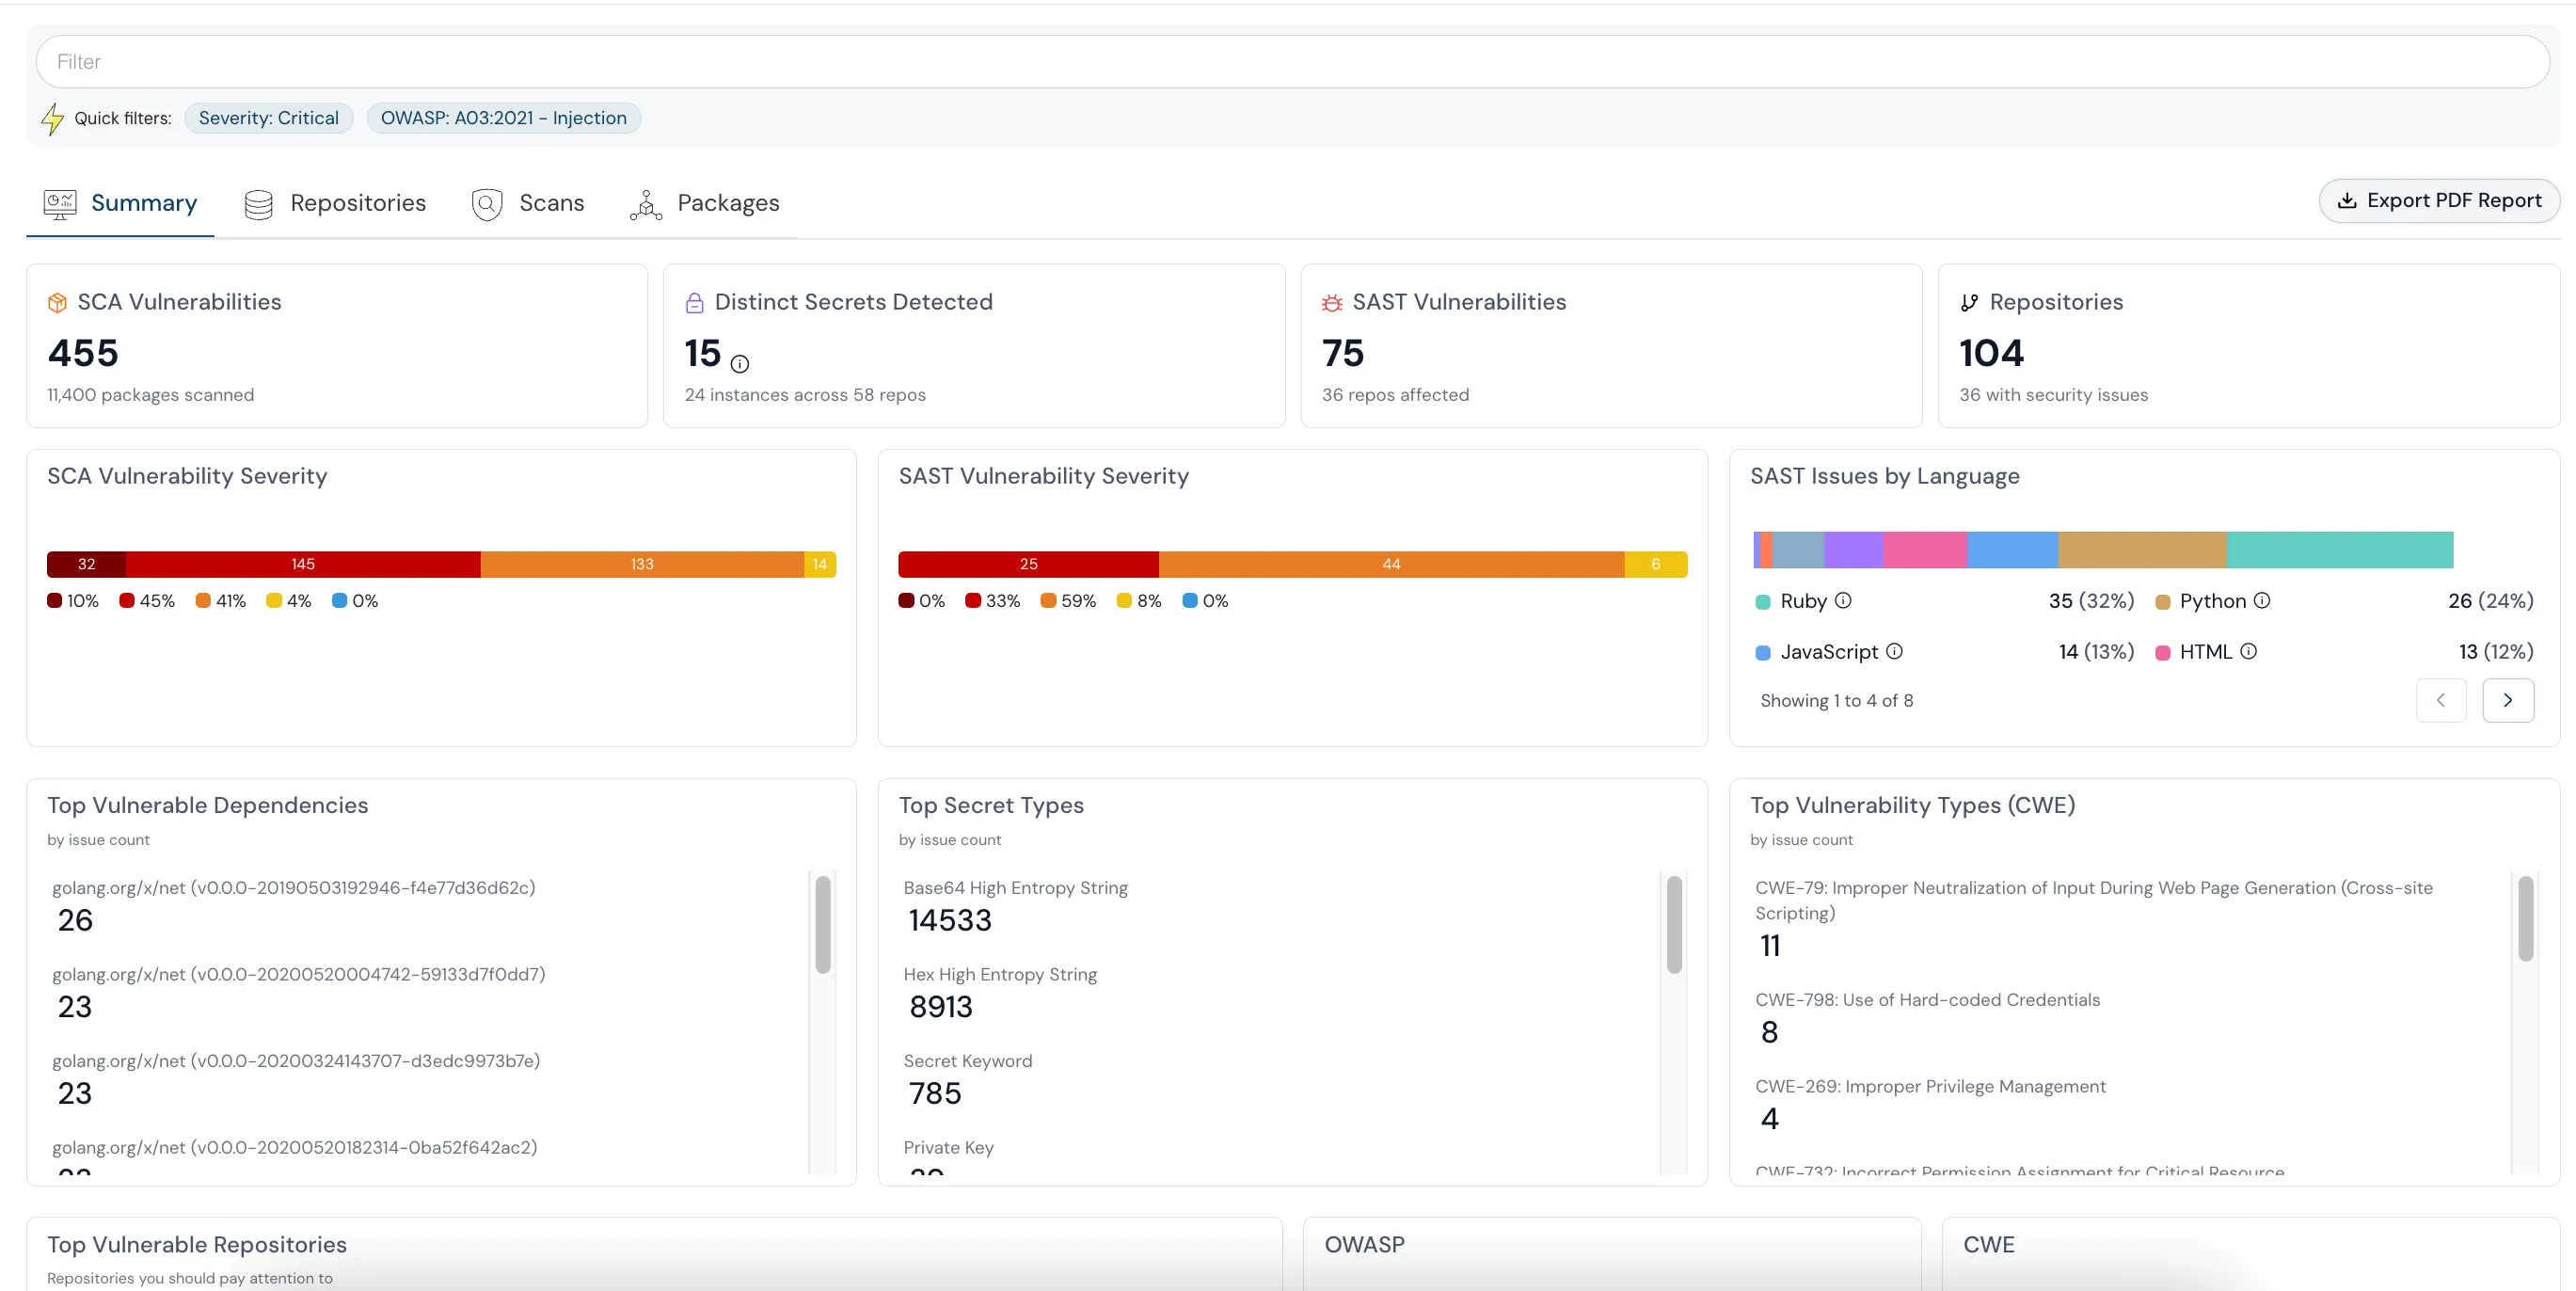
Cloudanix Code Security — Quality gate status on the pull request

Remediation Guidance, Not Just a Finding ID

Each finding carries actionable context — which version to upgrade to and whether it breaks, the secure alternative for a code pattern — with selective AI-generated fixes for safe cases, so the developer can resolve it inside the review rather than filing it for later.
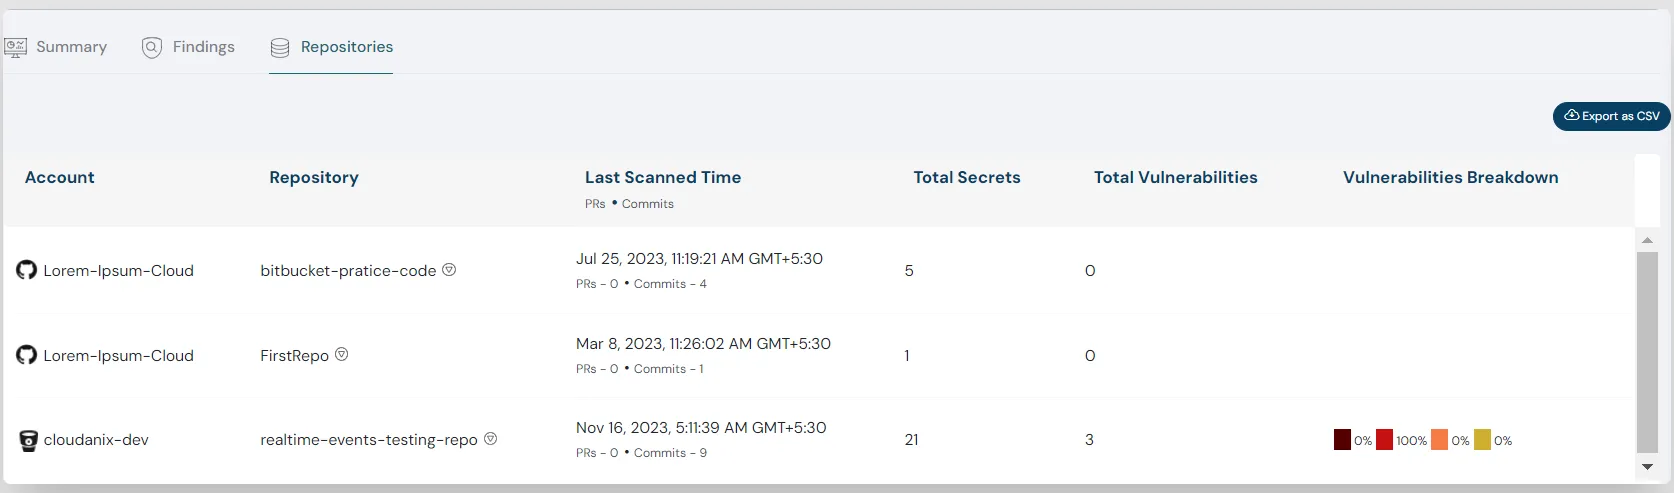
Cloudanix Code Security — Remediation guidance inline

Consistent Across Every Bitbucket Repository

Because gate and scan configuration can be set at the tenant level and overridden per repository, the same depth of MR feedback applies across every repo from one place, rather than being configured by hand — so the experience developers get is consistent wherever they are working.

Platform Impact

DimensionHigh-Level MR SignalDetailed PR-Time Findings
What the MR shows“Vulnerabilities found”Dependency, version, line, severity, fix
Developer workflowLeave review, open dashboardResolve inside the review
EnforcementAdvisory onlyConfigurable blocking gate
RemediationResearch taskGuidance and safe fixes inline
ConsistencyPer-repo manual setupTenant default, per-repo override

Why Detail at the MR Is the Whole Point of Shift-Left

Shift-left is often described as “scan earlier,” but the deeper idea is “give developers what they need to fix it where they already are.” A merge request that only says “there’s a problem” has shifted the timing left without shifting the context — the developer still has to go elsewhere to act. Carrying the full finding into the MR, with a gate behind it, is what makes the review the actual point of remediation. That is where a lean team recovers the most time: issues get fixed in the pull request, not filed into a backlog that never clears.

Key Outcomes

  • ✅ Detailed MR Findings: Dependency, version, line, severity, and fix — in the review.
  • ✅ Blocking Quality Gate: Configurable thresholds that fail the merge, not just warn.
  • ✅ Inline Remediation: Guidance and safe fixes where the developer is working.
  • ✅ Consistent Everywhere: Tenant defaults with per-repository overrides.
  • ✅ Less Context Loss: No handoff from the merge request to a separate dashboard.

Is Your Merge-Request Security Signal Too Thin to Act On?

If your Bitbucket merge requests say “vulnerabilities found” without the detail to fix them, Cloudanix posts the full finding and a configurable quality gate right in the review — so developers resolve issues before they merge.

Book a Free Assessment to see detailed merge-request scanning on your Bitbucket repositories, or explore the interactive demo on the Code Security page.


Related Resources

What Our Users Are Saying

Customer Reviews

Cloudanix is trusted by security leaders worldwide to deliver proactive, reliable, and cutting-edge cloud security.

One day, I changed the password of a root account, and my CTO called me within less than a minute to confirm if I did so. I was not expecting a reaction this quick. He told me Cloudanix alerted him of this password change and that he wanted to confirm as it was a critical security notification. I couldn't believe it!

Ritesh Agarwal
Ritesh Agarwal
CEO, Airgap Networks

Compliance is one way of staying secure, but what I want is the ability to go deeper and attain 'true security.' Cloudanix provides us the capability to do so.

Vishal Madan
Vishal Madan
Head of Engineering, iMocha

Cloudanix is building for the future of the cloud, which makes the product all the more desirable.

Ritesh Agarwal
Ritesh Agarwal
CEO, Airgap Networks

Cloudanix gave us the visibility we were missing. Being able to move from permanent access to a robust Just-In-Time (JIT) workflow has fundamentally changed our security posture without slowing down our engineering velocity.

Pavan Kumar Lekkala
Pavan Kumar Lekkala
SRE Lead, HugoHub

We are excited to leverage Cloudanix's comprehensive multi-cloud DevSecOps solution to secure our production workloads on AWS. Cloudanix has demonstrated that it can solve many challenges that DevSecOps teams face while continually adding new features such as SOC2 compliance and drift detection.

Satish Mohan
Satish Mohan
Co-founder & CTO, Airgap Networks

Managing third-party partner access was once a major concern for our security posture. With Cloudanix JIT Cloud, we've effectively achieved zero third-party risk. We can now grant access confidently, knowing that it is temporary, audited, and automatically revoked, resulting in a 100% reduction in our privileged access exposure.

Okesh Badhiye
Okesh Badhiye
Head of Technical Engineering, Finfinity

The snooze feature and responsible alerts have helped us save time and prioritize what to tackle first.

Satish Mohan
Satish Mohan
Co-founder & CTO, Airgap Networks

Implementing Cloudanix JIT internally allowed us to practice what we preach. By eliminating permanent access to our own clouds and databases, we've neutralized the risk of standing privileges, ensuring our own 'keys to the kingdom' are never left exposed.

Girish Manghnani
Girish Manghnani
Managing Partner, Tech Inspira

The problem with permissions is a lot of times, the gaps are left open due to oversights from inside the organization itself. With Cloudanix's CIEM, we get a complete view of user permissions and access. This enables us to update the permissions, reducing the attack surface.

Nilesh Pethani
Nilesh Pethani
Application Architect, iMocha

In the world of Fintech, trust is our currency. Cloudanix provided the frictionless visibility we needed to secure our EKS workloads across AWS, ensuring we stay audit-ready for SOC2 and GDPR without slowing down our engineering velocity.

Amol Naik
Amol Naik
Head of Security & Infrastructure, HugoHub

Cloudanix delivered value within 5 minutes of onboarding. Continuous monitoring, timely detection, and excellent documentation helped us attain a great cloud security posture.

Divyanshu Shukla
Senior DevSecOps, Meesho

Technology strategies and business strategies are in a state of constant change which includes centralization and decentralization of responsibilities. Regardless of strategic shift, we still have intellectual property to protect. Cloudanix are critical partners for us in our public cloud security posture across our three cloud providers.

Jerry Locke
Jerry Locke
Senior Director Global Solutions Engineering, Eversana

Cloudanix has been amazing. They opened up a common Slack channel with us — and it feels like we are talking to our own team and getting things done with Cloud security. The support team is always available, friendly, helpful, and ready to go out of their way.

Satish Mohan
Satish Mohan
CTO, Airgap Networks

Beyond just access management, Cloudanix CSPM has given us a unified view of our AWS environment. The real-time alerting and anomaly detection allow us to prevent any untoward activity before it happens, which is critical for a marketplace connecting 50+ financial institutions.

Okesh Badhiye
Okesh Badhiye
Head of Technical Engineering, Finfinity

For a Fintech company, data is our most valuable — and most sensitive — asset. Cloudanix DAM hasn't just improved our visibility; it has given us control. The ability to mask data and prevent unauthorized queries in real-time is a game-changer for our compliance and customer trust.

Jiten Gala
Jiten Gala
President Engineering and Product, Kapittx

Our clients, especially in the Middle East financial sector, demand absolute accountability. Cloudanix JIT Cloud has been a competitive differentiator for us, allowing us to provide secure, governed access to customer accounts that meet their strictest audit and compliance requirements.

Girish Manghnani
Girish Manghnani
Managing Partner, Tech Inspira

Cloudanix is always on my team's lips because of its exceptional support. Be it a small or big query, Cloudanix has gone above and beyond to resolve them. This one's a keeper for us.

Sujit Karpe
Sujit Karpe
CTO, iMocha

For a long-lasting partnership, great support goes a long way. Cloudanix has delivered exceptional support whenever required. Their edge is their team is always ready to go beyond to solve any issues that we have. This speaks volumes about the culture at Cloudanix.

Akash Maheshwari
Akash Maheshwari
Co-founder, MoveInSync

Beyond the technology, Cloudanix feels like an extension of our own team. Their willingness to stand up a dedicated Middle East tenant for us and provide exceptional support at a sensible price makes them a long-term partner for Hugosave.

Surya Tamada
Surya Tamada
CTO, HugoHub

The real-time notifications that Cloudanix provides are a real lifesaver. Their adaptive notifications ensure that my team stays productive and doesn't get interrupted all the time.

Digvijay Singh
Staff Security Engineer, Meesho

The whole point in technological evolution is to help improve the world we live in. We must protect that and to do so requires an effective and efficient security strategy. The Cloudanix team helped make our public cloud security posture management strategy a reality. The symbiotic relationship we have allows for a continuous feedback loop which is how business should operate.

Larry Wheat
Larry Wheat
Staff Solutions Engineer, Eversana

Ready to see your graph?

Connect a cloud account in under 30 minutes. See every finding rooted in identity, asset, and blast radius — with a fix path attached.

Book a Demo











