
Increased productivity and visibility
Recently, several nations and businesses have been affected by data breaches, and according to statistics, human error accounts for 95 percent of cybersecurity breaches. This highlights how important it is for employees to be aware of the possible consequences that can protect their infrastructure from outside attacks.
In the past month, we have made significant progress on several new features and enhancements.
Here are some highlights
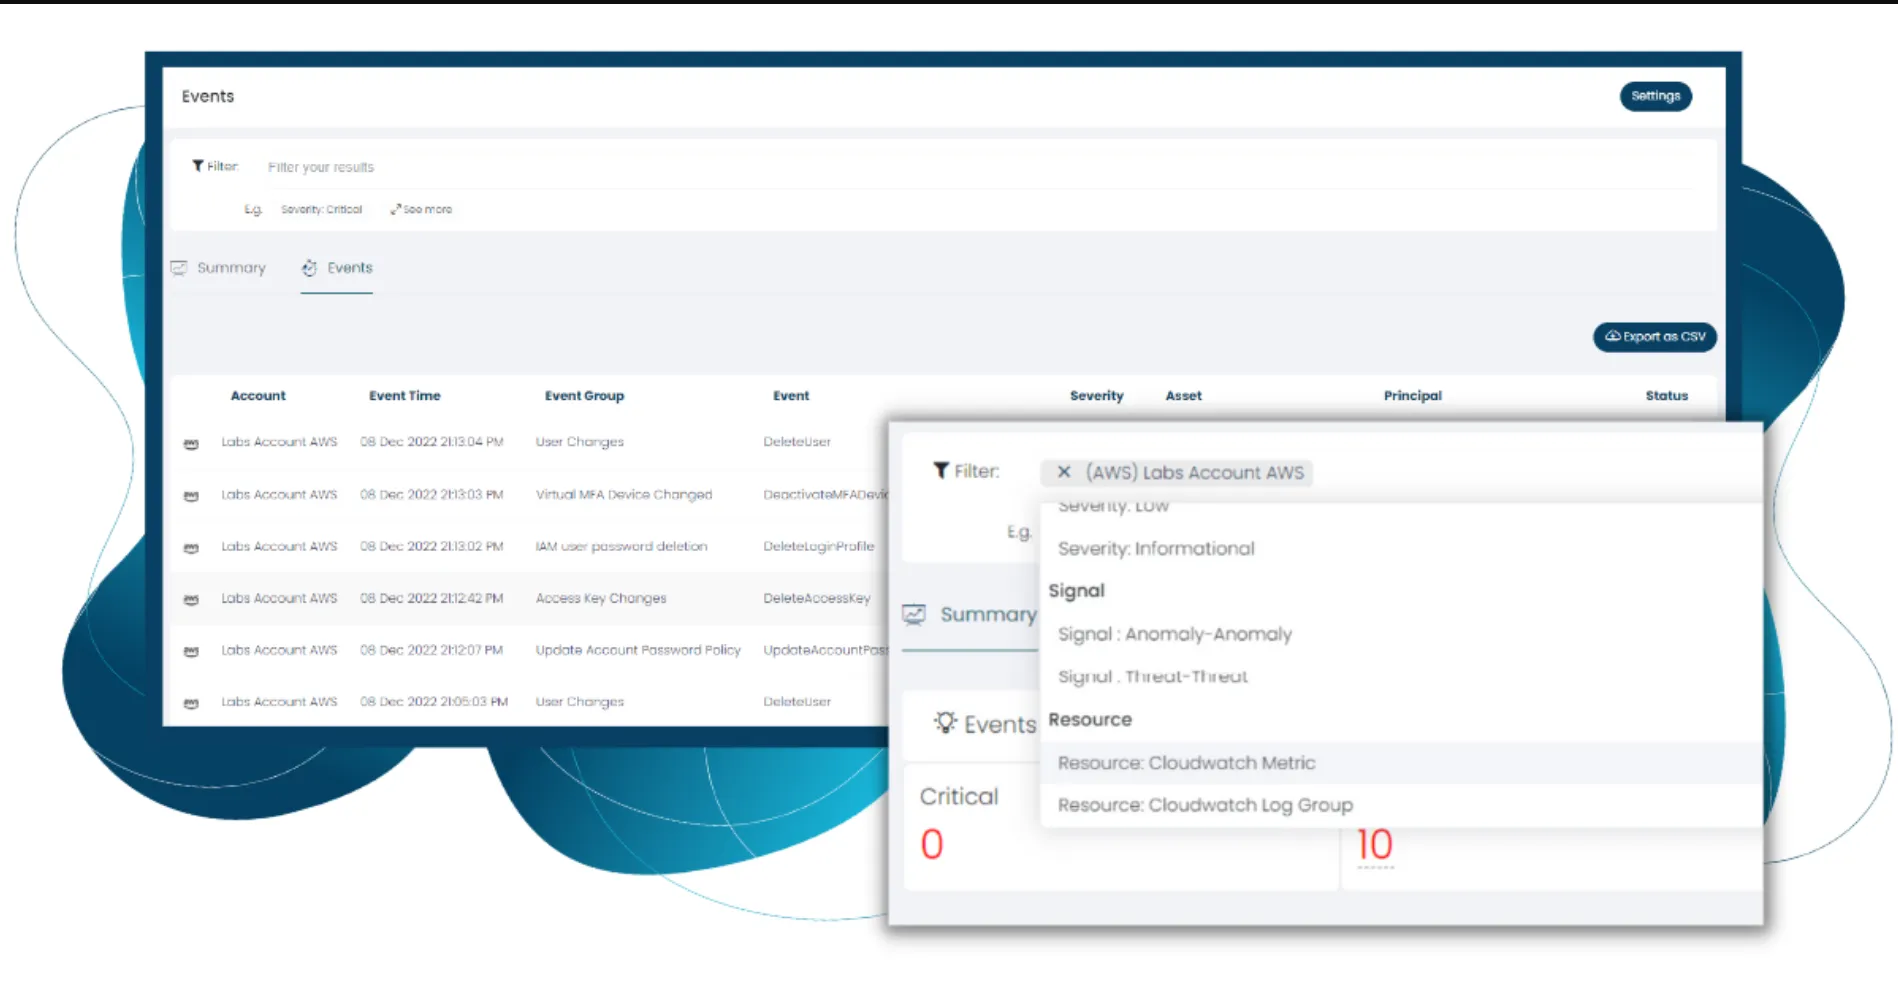
Container notification - Cloudanix dashboard
Predefined Views for focused work
With our pre-build views, customers can focus on the most important risks. Reach out to us to build more of these and we can roll them out for you. (shhhh .. we are soon rolling out an ability for you to build your own queries and views)
Enhanced Azure realtime monitoring
Additional rules supported, including events occurring in the Azure Active Directory. e.g Login without MFA, New role assignment as owner, etc.
IAM + Events
You can see the events initiated by the Principal right from the IAM screens.
Ready to see your graph?
Connect a cloud account in under 30 minutes. See every finding rooted in identity, asset, and blast radius — with a fix path attached.
Book a DemoBlog
Read More Posts
Your Trusted Partner in Data Protection with Cutting-Edge Solutions for
Comprehensive Data Security.
Wednesday, Oct 21, 2026
GhostAction: Malicious GitHub Actions Workflows Hit 30,000 Repos. Your CI/CD Is an Identity Problem
A credential-theft campaign tracked as GhostAction has been planting malicious GitHub Actions workflows into open-so
Read More
Wednesday, Oct 21, 2026
CISA Flags an Ivanti Connect Secure Zero-Day: Why the Fix Is Exposure and Blast Radius, Not Just the Patch
On October 13, 2026, CISA added a newly exploited Ivanti Connect Secure flaw — CVE-2026-104935 — to its [Known Explo
Read More
Wednesday, Oct 21, 2026
Nikkei's Third Breach in a Month: When Stolen Credentials Reach a Cloud Dev Service
On October 16, 2026, Nikkei Inc. disclosed its [third data breach within a month](https://www.rescana.com/post/nikkei-in
Read More