APRA, the Australian Prudential Regulation Authority, is an independent statutory authority responsible for supervising institutions across the Australian financial services industry, including banks, credit unions, insurance companies, pension funds, etc. APRA compliance refers to adhering to regulations set forth by APRA.
The primary goal of APRA is to ensure the financial stability and soundness of these institutions and provide confidence to the consumers in the financial institutions.
What Entities are Regulated by APRA?
The Australian Prudential Regulation Authority (APRA) regulates various institutions within the Australian financial services industry. We have listed 6 key entities that APRA regulates. Let us understand how APRA regulates them all. Remember, APRA may also regulate specific activities or institutions within the broader financial services landscape.
Authorized Deposit-taking Institutions (ADIs)
ADIs encompass traditional banks, building societies, and credit unions. APRA ensures these institutions maintain sufficient capital reserves to sustain withdrawals and economic downturns, protecting depositors’ money.
Insurance Companies
APRA supervises both general and life insurance companies. Regulations ensure the institution’s ability to meet financial obligations and keep fair treatment of policyholders. Practices include capital adequacy requirements, risk management practices, and consumer protection measures.
Superannuation Funds
Superannuation also refers to Australia’s retirement savings system. This does not include self-managed funds. Most of the superannuation funds are taken care of by APRA ensuring they are managed prudently and deliver sustainable retirement benefits to members. Regulations focus on investment strategies, risk management, and member protection.
Friendly Societies
Friendly societies are generally referred to as mutual organizations providing financial services and benefits to their members, often focusing on specific communities or professions. APRA regulations ensure their financial soundness and adherence to fair practices towards members.
Private Health Insurance
Companies that offer health insurance coverage are regulated under APRA’s watch. Regulations address solvency, risk management, and consumer protection to ensure fair pricing and quality service for policyholders.
Reinsurance Companies
Reinsurance companies are the companies that provide insurance to other insurance companies, this acts as a risk buffer. APRA ensures the stability of this sector by regulating capital adequacy and risk management practices.
Assess Your APRA Compliance Status
What are APRA Standards?
APRA Standards are a set of rules legally binding regulations established by APRA to ensure the financial stability and soundness of institutions within the Australian financial services industry. These standards define the rules primarily for banks, insurance companies, superannuation funds, and other entities under APRA’s supervision.
Primary Focus
The key areas that APRA primarily focuses on are as follows:
Capital Adequacy: Institutions must maintain sufficient financial reserves to handle potential losses and economic challenges.
Effective Risk Management: Implementing robust security practices to identify, assess, and mitigate risks faced by the institution.
Strong Governance: Sound decision-making and accountability within the institution’s leadership.
Prudential Reporting: Accurate and timely financial reporting to APRA.
Consumer Protection: Ensuring financial services customers get fair and responsible treatment.
Types of Standard
There are two main types of standards categorized into Prudential Standards (CPS) and Prudential Guideline (CPG).
Prudential Standards (CPS): These are legally binding requirements that set minimum guidelines for areas like capital adequacy, risk management, governance, and reporting.
Prudential Guidelines (CPG): CPG provides guidance and best practices for organizations to stick to the standards, but are not legally binding.
APRA publishes a comprehensive list of all its standards, including the date of the latest version, on its website.
The APRA Standards That Matter Most for Cloud and Security Teams
Two prudential standards are especially relevant if you run regulated workloads in the cloud:
CPS 234 — Information Security
CPS 234 requires APRA-regulated entities to maintain information security capabilities commensurate with the size and threat profile of their operations. In practice it means you must:
- Clearly define information security roles and responsibilities, including where a third-party cloud provider manages information assets on your behalf.
- Implement controls to protect information assets and test their effectiveness through a systematic testing program.
- Notify APRA of a material information security incident, typically within 72 hours.
For cloud teams, CPS 234 maps directly to continuous configuration monitoring (CSPM), identity and entitlement controls (CIEM/JIT), and evidence you can produce on demand.
CPS 230 — Operational Risk Management
CPS 230, effective 1 July 2025, consolidated five older standards (covering outsourcing and business continuity) into a single operational-resilience standard. It requires entities to identify critical operations, set tolerance levels for disruption, and — importantly for cloud — actively manage the risk of material service providers, including the cloud platforms and SaaS vendors your critical operations depend on.
Together, CPS 234 and CPS 230 push regulated Australian entities toward continuous, evidence-backed monitoring of both their own cloud posture and their third-party/cloud dependencies.
Benefits of Adhering to These Standards
By adhering to APRA standards, organizations can get the following benefits:
Financial Stability: A more robust and resilient financial system for Australia.
Consumer Confidence: Increased trust and confidence in the financial services industry.
Reduced Risk: Lower risk of financial institution failures that can negatively impact depositors, policyholders, and the broader economy.
Learn About Cloud Compliance for APRA
How APRA Standards Translate Into Cloud Controls
For an engineering team, “comply with CPS 234” is not an actionable instruction. What makes it actionable is mapping each expectation to a concrete cloud control you can implement and monitor.
Information security capability commensurate with threat. In cloud terms this is continuous posture monitoring. You need to know the configuration state of every account, Region, and service — and detect when something drifts out of a secure baseline. Cloud Security Posture Management (CSPM) is the mechanism, mapping live configuration to the controls CPS 234 expects. See What is CSPM?.
Clearly defined roles, including third parties. CPS 234 explicitly contemplates that a cloud provider may manage information assets on your behalf. That means documenting the shared responsibility model boundary — what the provider secures versus what you secure — and proving you control your side.
Access controls and least privilege. Regulated financial data demands that access be tightly scoped and auditable. CIEM right-sizes entitlements to actual usage, and just-in-time access removes standing privilege so that access to sensitive systems is granted for a bounded window and revoked automatically — each grant logged as evidence. For database-resident financial and customer data, Database Activity Monitoring with PII masking demonstrates that access to sensitive records is watched.
Systematic testing of controls. CPS 234 expects you to test that controls actually work, not just that they exist. Continuous monitoring plus documented remediation gives you an ongoing testing record rather than an annual snapshot.
Incident notification. CPS 234 requires notifying APRA of a material information security incident, typically within 72 hours. That is only achievable if you can detect and scope an incident quickly — which depends on Cloud Detection and Response, behavioral UEBA, and attack-path context to understand blast radius fast.
Material service provider management (CPS 230). Because CPS 230 makes you responsible for the resilience of the cloud platforms and SaaS vendors your critical operations depend on, you need a live inventory of those dependencies and their security posture — not a spreadsheet updated once a year.
Preparing for APRA Scrutiny
APRA supervises actively, and it can — and does — take action against entities whose practices fall short, including through enforceable undertakings, additional capital requirements, and public findings. Rather than fixate on penalties, regulated entities are better served by being able to demonstrate control at any time. Practical steps:
- Centralize evidence. Keep configuration history, access logs, and remediation records in one place so you can produce them on request rather than reconstructing them under pressure.
- Treat compliance as continuous. A point-in-time attestation says little about the state of a fast-changing cloud environment. Continuous monitoring is what matches APRA’s expectation of an ongoing capability.
- Map controls once, satisfy many frameworks. Australian financial entities often carry APRA obligations alongside ISO 27001, SOC 2, or PCI DSS. The underlying controls overlap heavily; implement them once and reuse the evidence. See What is Cloud Compliance?.
- Know your material service providers. Maintain a current view of the cloud and SaaS dependencies behind your critical operations, since CPS 230 puts their resilience within your responsibility.
How Cloudanix Helps with APRA Compliance
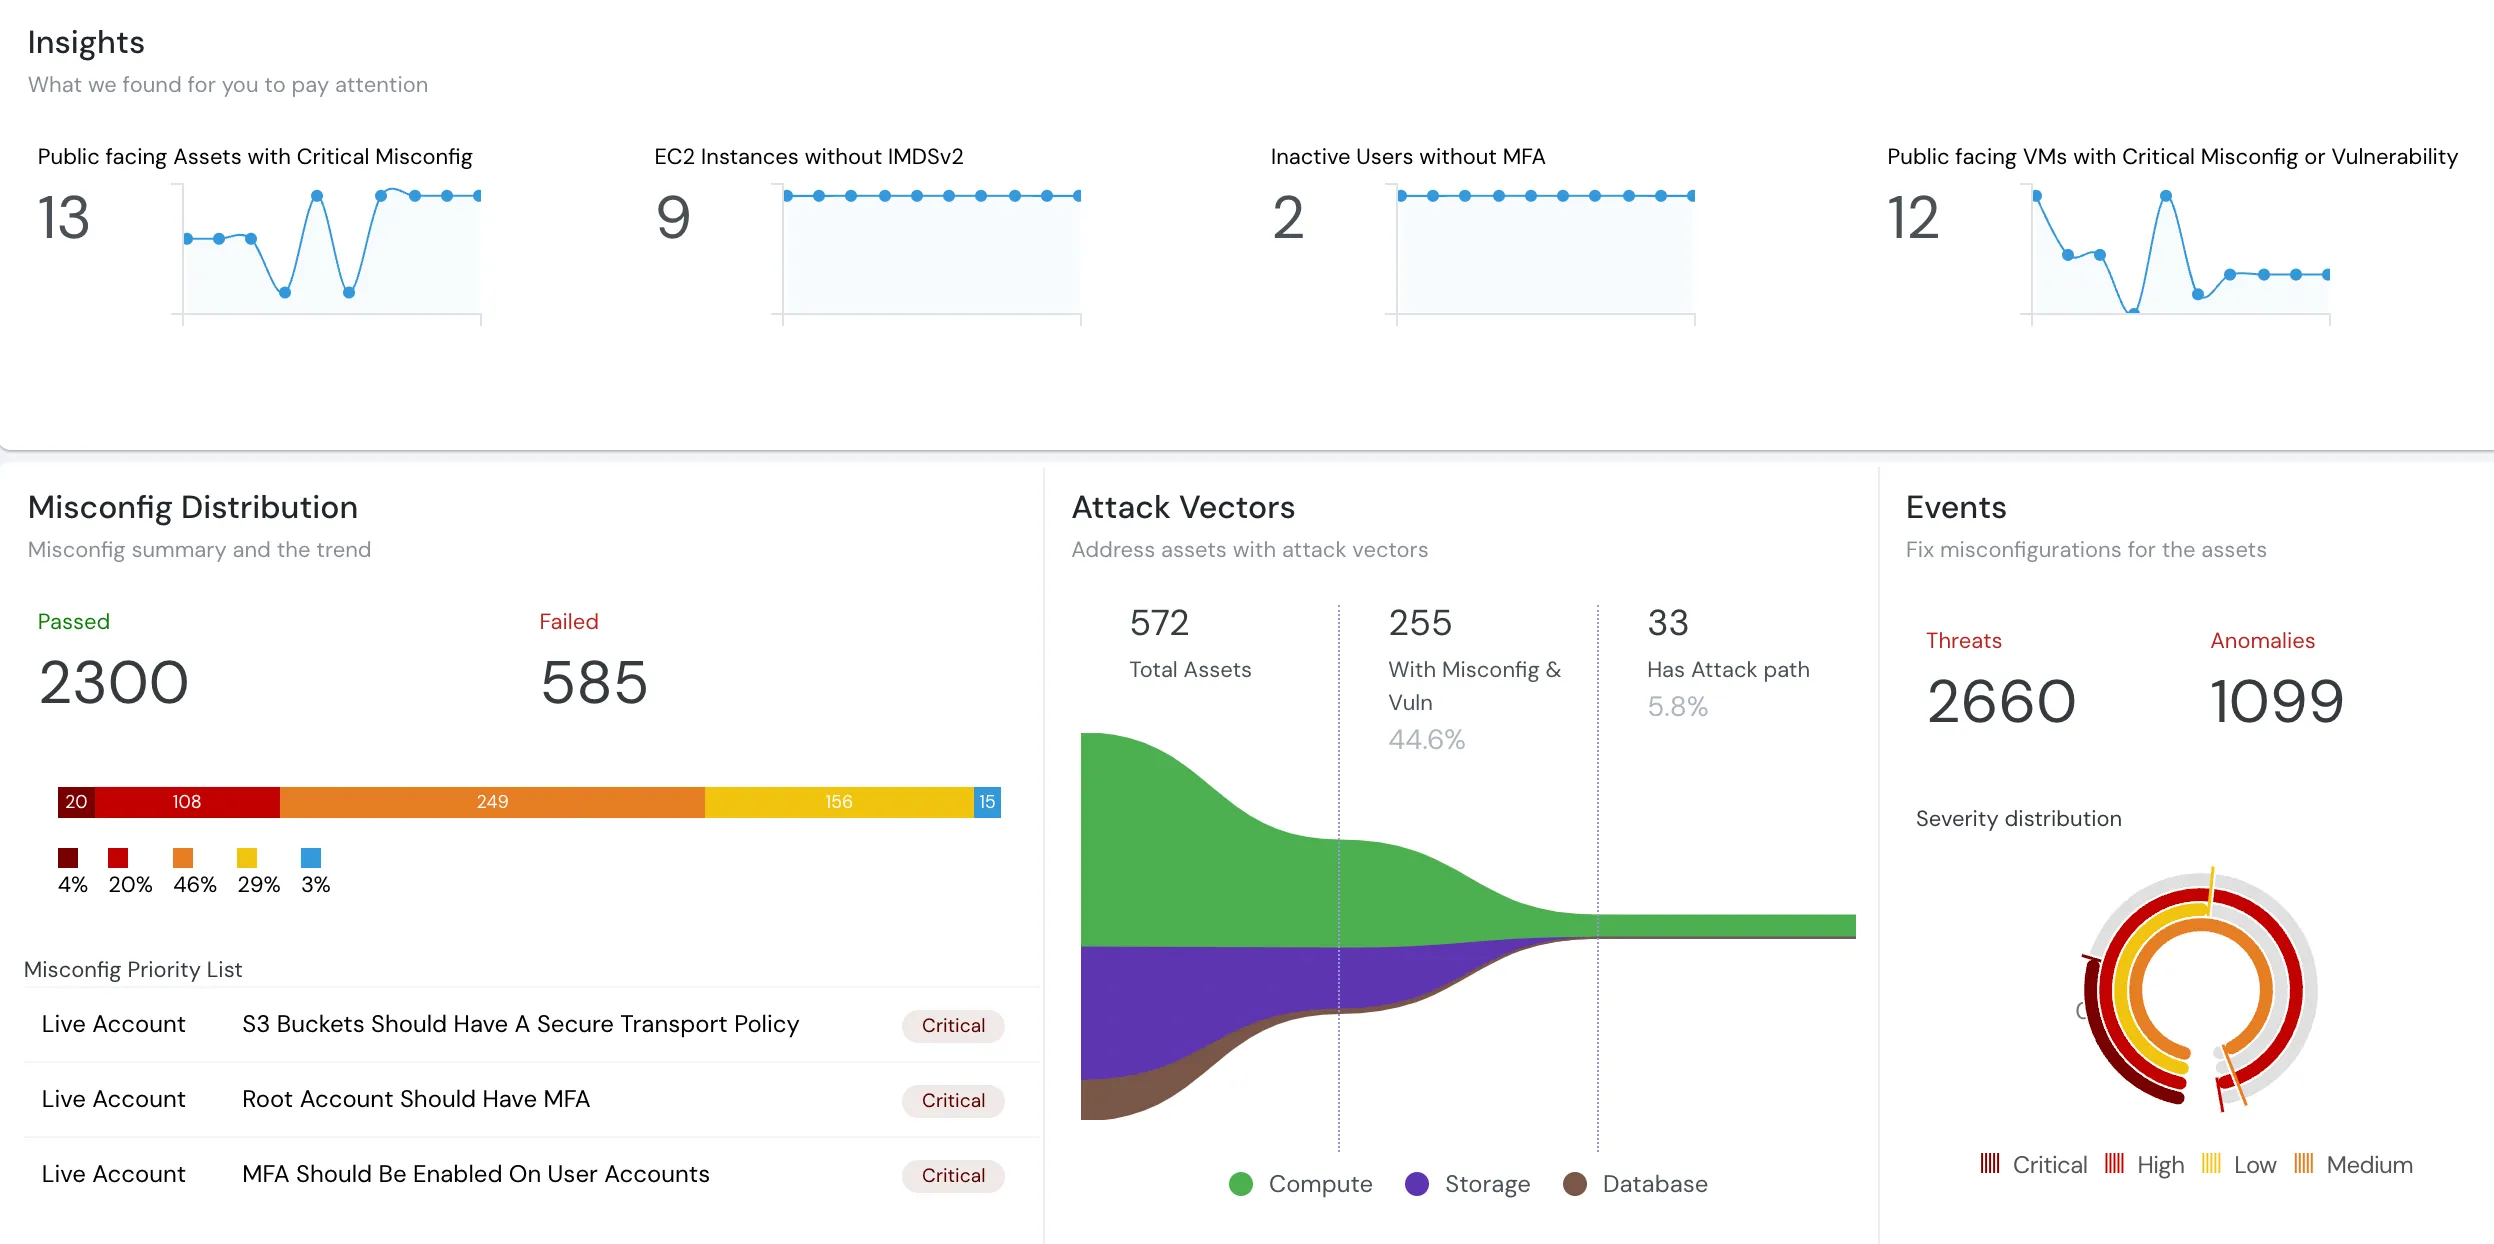
Cloudanix maps your live cloud posture to APRA-relevant controls — CPS 234 information security and CPS 230 operational-risk expectations — alongside 15+ other frameworks from a single platform. Continuous CSPM monitoring catches misconfiguration and drift as it happens; CIEM and just-in-time access enforce and evidence least privilege; Database Activity Monitoring protects sensitive financial and customer data with PII masking; and CDR with UEBA shortens the detection and scoping window that a 72-hour notification obligation demands. When APRA — or an auditor — asks for proof, audit-evidence export turns the request into a download. Explore Cloudanix APRA compliance.