
Identity and Access Management - The New Edge of Security
The network is not the perimeter. Identity is the perimeter.
Identity and Access Management (IAM) has traditionally been considered one of the boring parts of security. But with the rise in the field of cloud computing, IAM has become increasingly important and is now referred to as “the new edge of security.”
Earlier, network security controls such as firewalls and IP restrictions were the primary means of protecting systems and data. However, cloud environments limit visibility and control over the networking layer, making traditional perimeter defenses less effective.
Cloud-based models allow for broader and more distributed access, increasing the attack surface and complicating access control.
This is where IAM plays a critical role. IAM provides a centralized way to manage access to resources, whether those resources are on-premises or in the cloud. By implementing IAM, organizations can define and enforce who gets access to what, and under what conditions.
Why IAM is Crucial in the Cloud
Highlights from a ScaleToZero podcast episode featuring Chad:
- It is necessary to maintain control as applications and data migrate to the cloud.
- Cloud platforms offer limited built-in security controls, making IAM essential.
- IAM simplifies compliance by offering centralized access management.
- IAM reduces the risk of breaches by ensuring only authorized access to sensitive data.
If you are moving to the cloud or already operate in the cloud, a strong IAM strategy is essential.
Tips for Implementing a Strong IAM Program
- Implement IAM JIT (Just-In-Time): Team members should not have standing access. Access should be granted only when required.
- Define a Clear IAM Policy: Create strict access policies that are role-based and well-documented.
- Use Strong Authentication: Enforce MFA, hardware tokens like Yubikey, or access tokens.
- Monitor User Activity: Set up logging and alerts to detect suspicious behavior.
- Review IAM Policies Regularly: Ensure policies evolve with the organization’s needs.
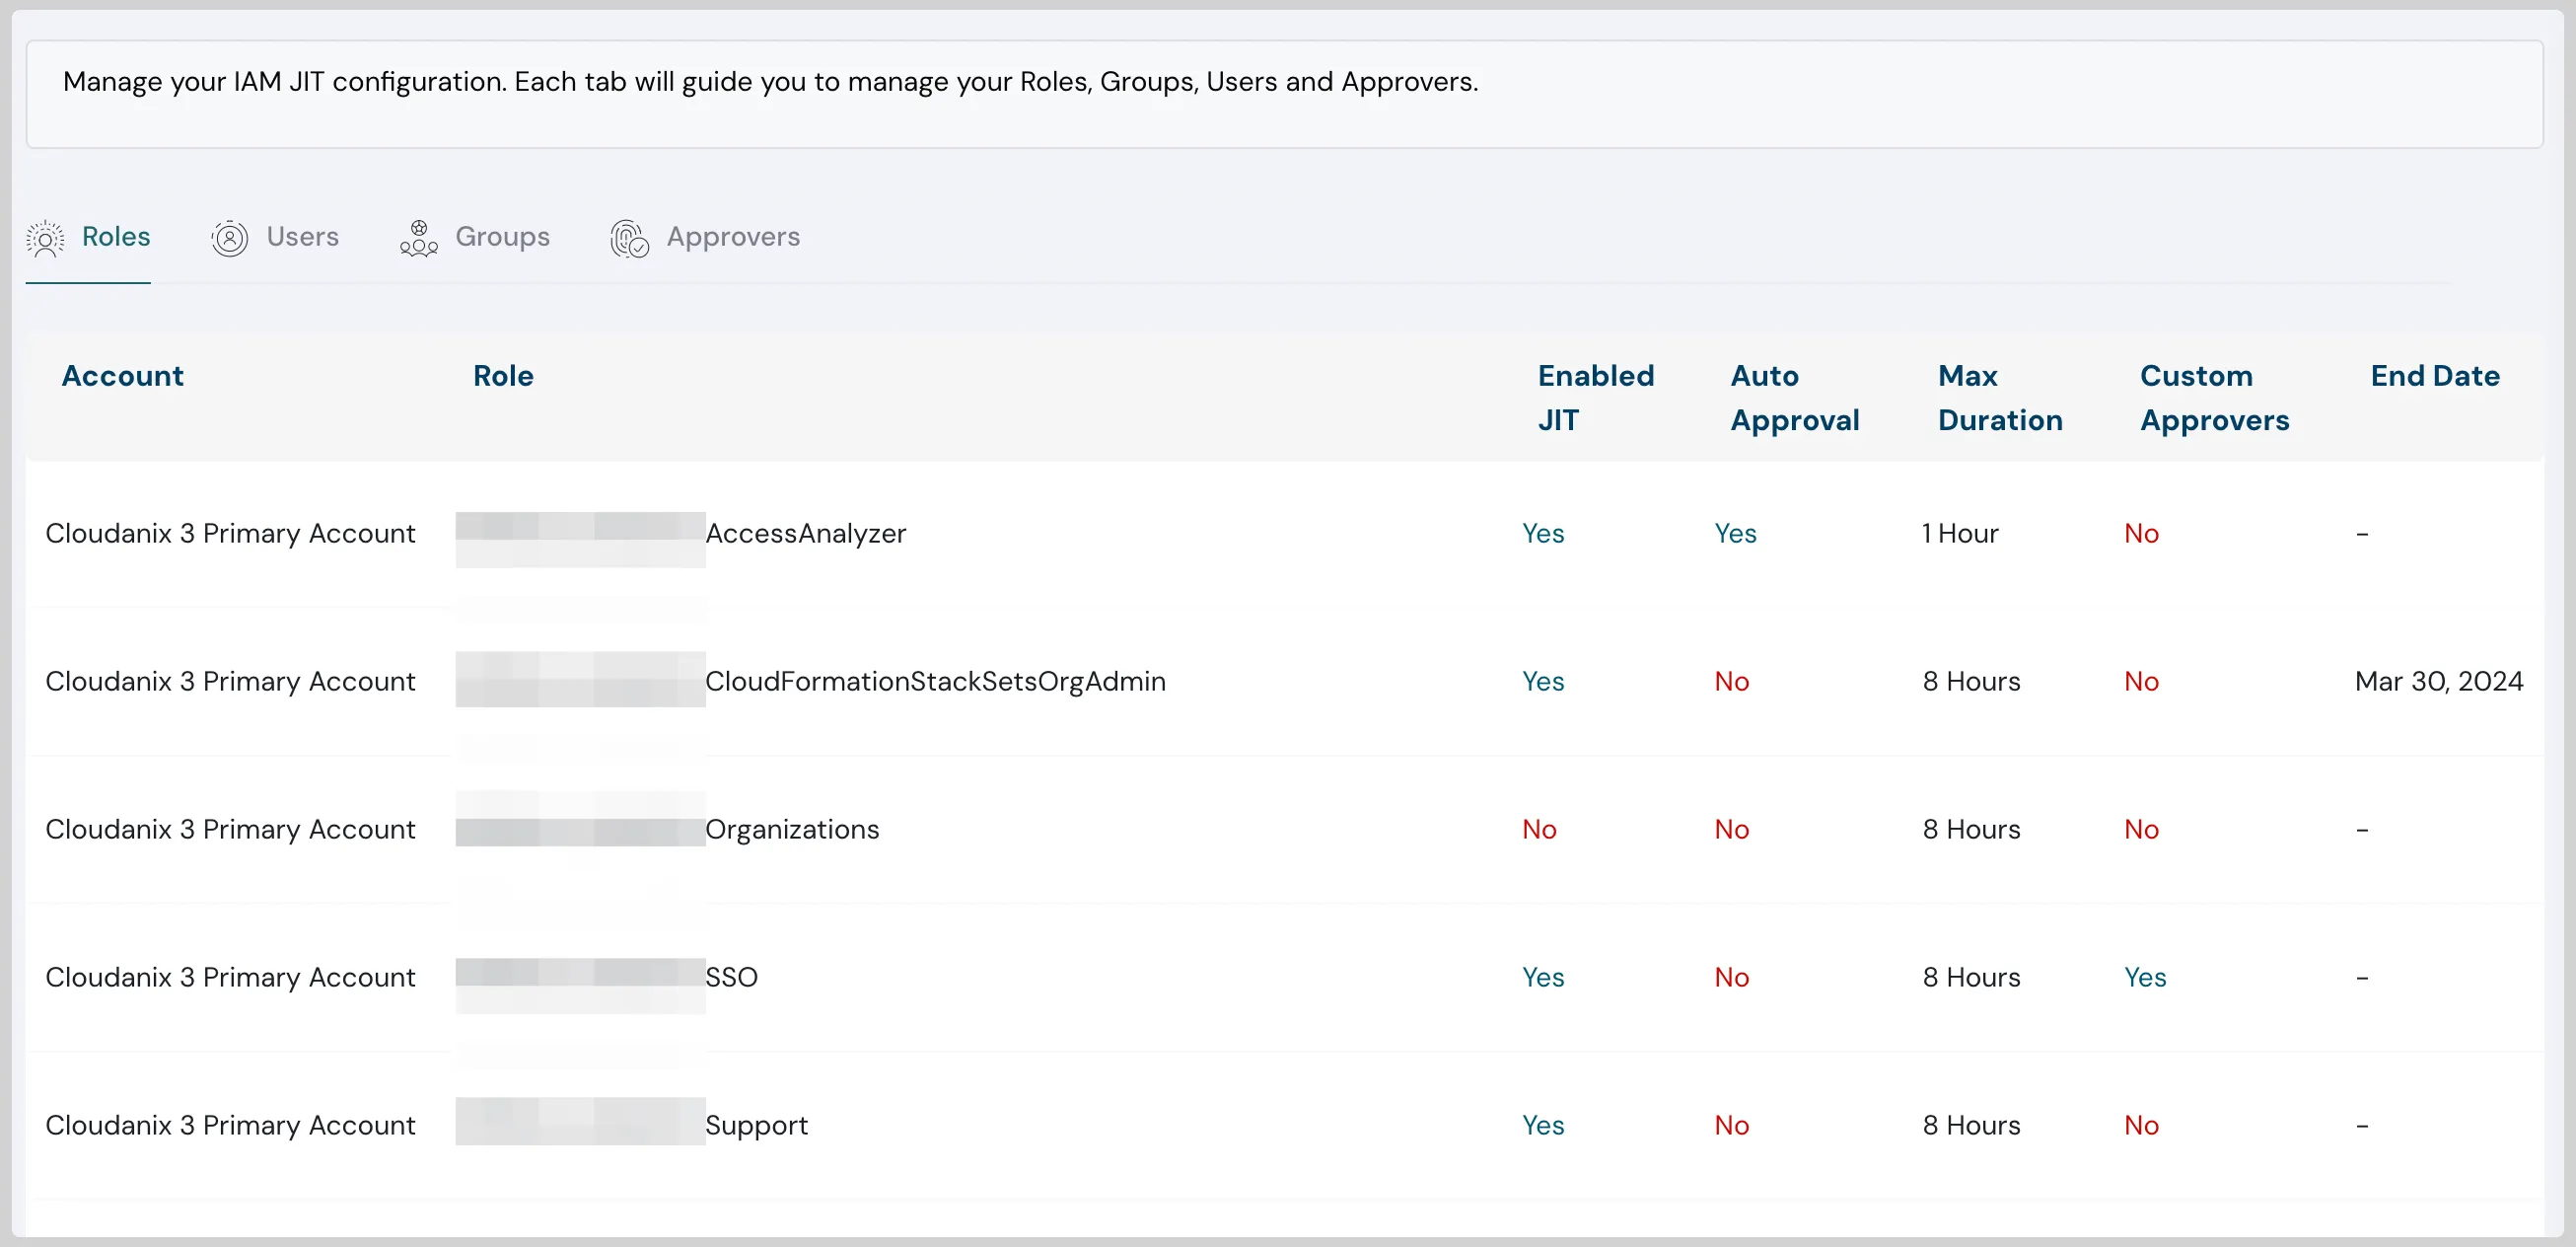
Cloudanix IAM JIT lets your team request limited-time access to permissions in just a few clicks, with full traceability and control.
How Has IAM Evolved in the Last Five Years?
IAM is no longer just about assigning permissions. Here’s how it’s changing:
- Proactive Security: Instead of reacting to incidents, organizations now anticipate and prevent IAM risks.
- IAM Automation: Tasks like provisioning and de-provisioning users are increasingly automated.
- IAM Security Tools: More tools are being used to detect and respond to IAM threats.
- Cloud IAM Adoption: Organizations need fine-grained control over access to cloud resources.
- Complex IAM Environments: As businesses scale, IAM must balance security with usability.
- Auditor Visibility with IAM JIT: IAM JIT helps auditors verify access logs, durations, and actions.
Communicating IAM’s Business Value to Stakeholders
Security teams must align IAM efforts with business outcomes to gain stakeholder support:
- Align with Business Goals: Show how IAM supports compliance, reduces fraud, and boosts innovation.
- Quantify the Impact: Highlight reductions in security incidents or operational costs.
- Use Simple Language: Avoid jargon when explaining IAM to non-technical audiences.
- Tailor Messages: A CFO, CTO, and CIO each care about different aspects of IAM.
Practical Ways to Communicate IAM Value:
- Build a business case that outlines cost, benefit, and risk reduction.
- Use dashboards that show IAM metrics: unauthorized access attempts, provisioning speed, etc.
- Share success stories of IAM helping achieve compliance or preventing incidents.
- Integrate IAM with the broader security strategy.
- Involve all departments in IAM policy development and training.
- Continually assess and optimize IAM performance.
Why “Identity is the Perimeter” Is More Than a Slogan
The phrase gets repeated so often it risks sounding like marketing. The underlying shift is concrete. In a traditional data center, an attacker had to defeat network controls — get past the firewall, onto the VLAN, through the segmentation — before touching anything valuable. Those controls were the perimeter, and they were largely under your physical control.
In the cloud, most services are reachable over the public internet by design. An S3 bucket, a managed database, an API gateway — they are all one authenticated request away from anyone with valid credentials. The thing standing between an attacker and your data is no longer a network boundary; it is whether the identity making the request is legitimate and authorized. That is why identity has become the control plane. When the network stops being a meaningful wall, the credential becomes the front door.
This also reframes what a “breach” looks like. Many cloud incidents involve no exploit at all in the classic sense. An attacker obtains a valid key or session token — through phishing, a leaked secret in a repo, or a compromised laptop — and then simply uses the cloud API the way a legitimate user would. Nothing is “hacked.” The identity layer was the perimeter, and it was crossed with a key rather than a crowbar.
The Cloud Entitlement Explosion
There is a structural reason identity is hard to get right in the cloud: the sheer scale of permissions. A single AWS account can offer thousands of distinct API actions across hundreds of services. Multiply that by multiple accounts, three cloud providers, and a mix of human and machine principals, and the number of possible identity-to-resource relationships becomes far too large to reason about by hand.
The result is that almost every cloud environment grants far more access than it uses. Permissions are added for a task and never removed. Broad managed policies get attached because they are easier than writing a scoped one. Roles accumulate. This gap between granted and used permission is the raw material of most identity-driven incidents, and it is exactly why the manual, role-by-role approach that worked on-premises does not survive contact with cloud scale. You need tooling that computes effective access and compares it to actual usage. See What is CIEM? for how entitlement management addresses this directly.
Human, Machine, and AI Identities
Treating “identity” as synonymous with “employee” is one of the most common blind spots. In a typical cloud estate, non-human identities — service accounts, workload roles, CI/CD pipelines, functions, and now AI agents — outnumber humans by a large margin. They authenticate with keys and tokens, they rarely have an offboarding process, and their credentials often outlive the projects that created them.
AI agents raise the stakes further. An agent that calls cloud APIs on its own needs an identity, permissions, and monitoring just like any other principal — but it can act at machine speed and in ways its operators did not explicitly script. Governing non-human identities with the same rigor as human ones, and monitoring their behavior for drift, is no longer optional for AI-forward engineering teams. See Understanding Non-Human Identities.
IAM JIT and Cloudanix
Cloudanix IAM Just-In-Time (JIT) ensures temporary, auditable, and secure access across your cloud platforms. Teams gain the right permissions at the right time with clear expiration and audit trails.
Concretely, that means:
- No standing privilege for sensitive actions. Access to production, databases, Kubernetes, and VMs is requested when needed and revoked automatically when the window closes.
- Right-sizing from real usage. CIEM analysis compares what identities can do against what they actually do, so you can trim entitlements to the permissions in use.
- Blast-radius context. The unified asset graph and attack-path analysis show whether an over-privileged identity actually reaches something valuable, so you fix the paths that matter first.
- Behavioral monitoring. UEBA baselines normal activity per identity and flags anomalies — a login from a new region, an unusual API pattern, a service account behaving like a person.
- Audit-ready evidence. Every JIT grant and revocation is logged and exportable for compliance, which is what regulated FSI and healthcare teams need to satisfy auditors.
Remember: In the cloud, the network is not the perimeter. Identity is. Cloudanix provides IAM security governance across AWS, Azure, and GCP — with CIEM analysis, JIT access, and identity blast-radius context.













