
Cutting Down Notification Noise with Container Updates
And now you can further cut down the noise with this new feature!
Recently, several nations and businesses have been affected by data breaches, and according to statistics, human error accounts for 95% of cybersecurity breaches. This highlights how important it is for employees to be aware of the possible consequences that can protect their infrastructure from outside attacks.
In the past month, we have made significant progress on several new features and enhancements.
Highlights
1. Container Notifications
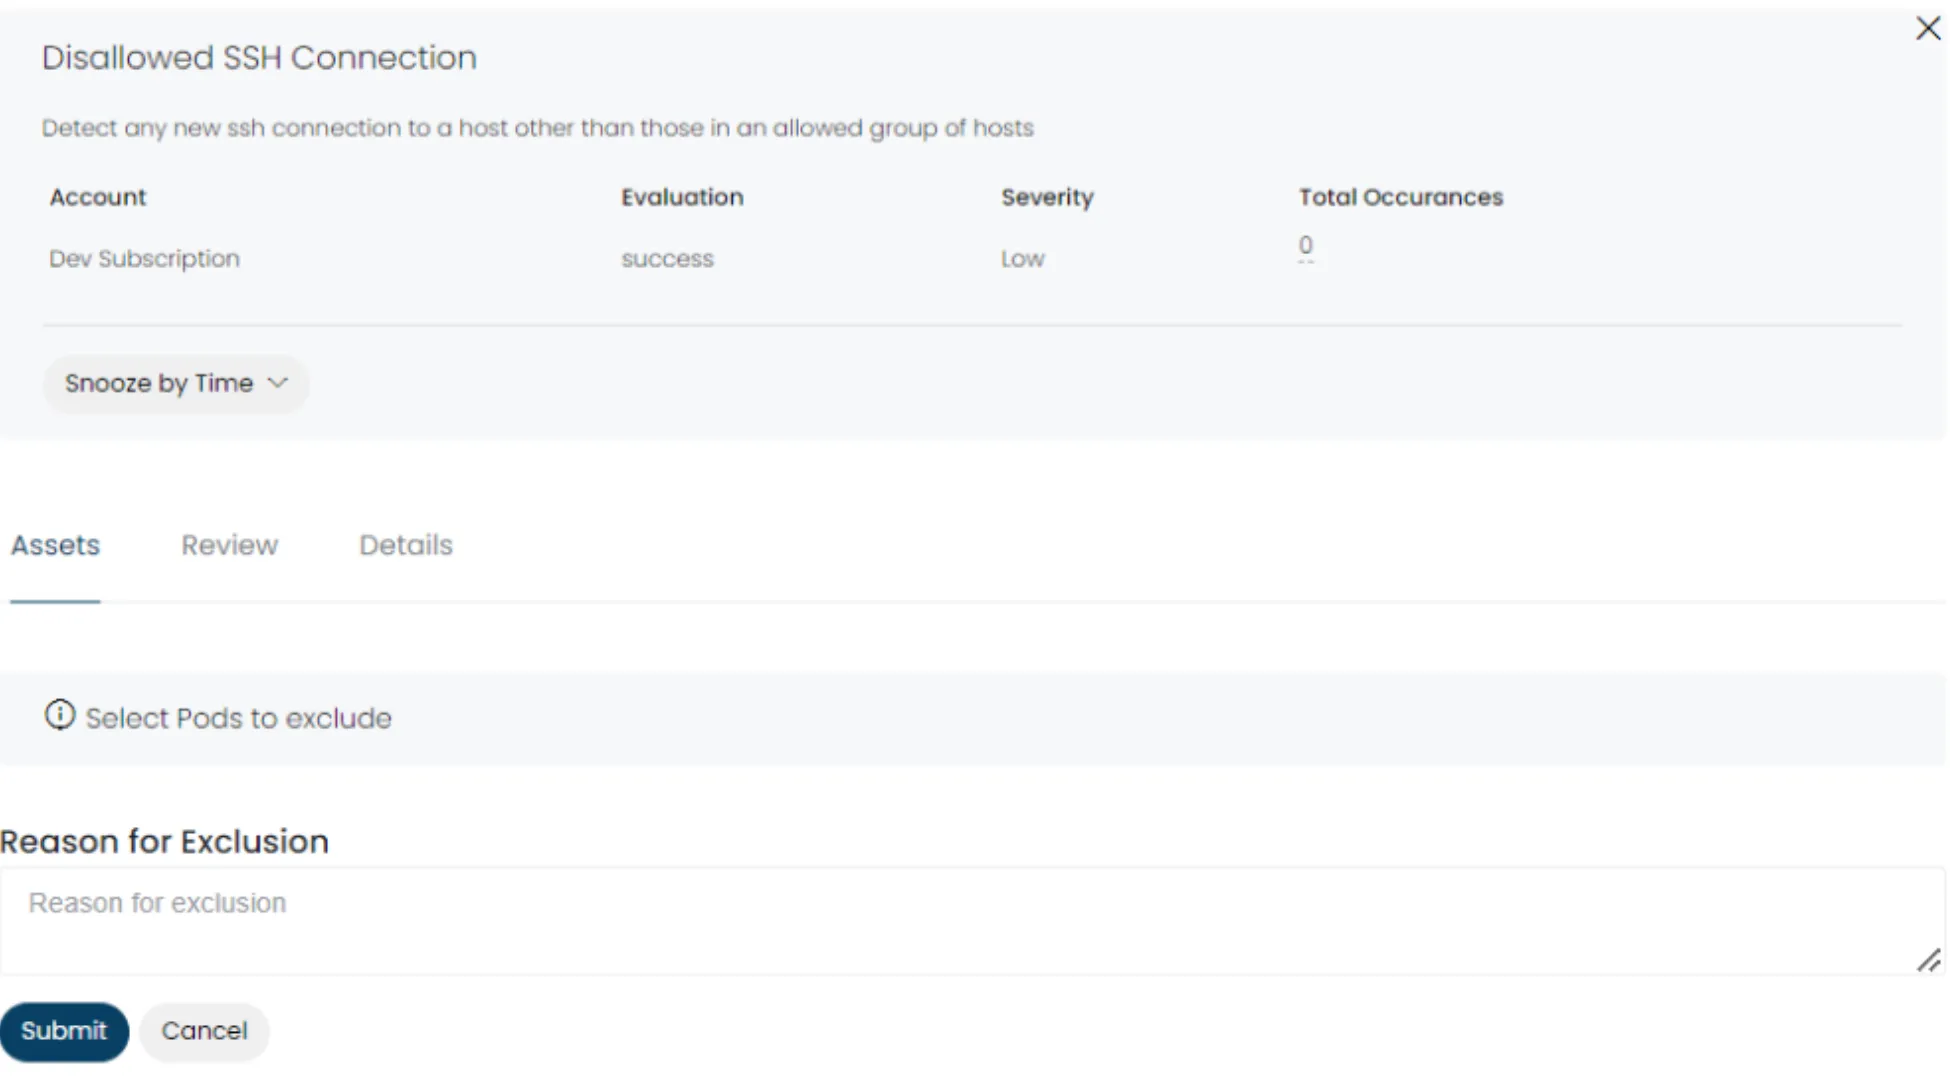
You can now mute notifications for your container workloads based on pods, containers, and nodes. This means you can receive more targeted alerts and cut down the noise.
2. Review Container Risks
We now support the same workflow for containers as we do for your Risk screens. You can:
- Acknowledge (and open a Jira ticket)
- Pause the risks
- Accept the risk
3. Better Events UX & Notifications
Events UX and notifications have been revamped to show additional information directly in Slack/Email, so you don’t have to come to the Dashboard. You can consume the information on the go.
4. Historical Data
On the Risk slide-out, you can now see historical assets that may have failed in the past. This helps track how risks have been affecting assets and how they have been remediated over time.
Ready to see your graph?
Connect a cloud account in under 30 minutes. See every finding rooted in identity, asset, and blast radius — with a fix path attached.
Book a DemoBlog
Read More Posts
Your Trusted Partner in Data Protection with Cutting-Edge Solutions for
Comprehensive Data Security.
Wednesday, Oct 21, 2026
GhostAction: Malicious GitHub Actions Workflows Hit 30,000 Repos. Your CI/CD Is an Identity Problem
A credential-theft campaign tracked as GhostAction has been planting malicious GitHub Actions workflows into open-so
Read More
Wednesday, Oct 21, 2026
CISA Flags an Ivanti Connect Secure Zero-Day: Why the Fix Is Exposure and Blast Radius, Not Just the Patch
On October 13, 2026, CISA added a newly exploited Ivanti Connect Secure flaw — CVE-2026-104935 — to its [Known Explo
Read More
Wednesday, Oct 21, 2026
Nikkei's Third Breach in a Month: When Stolen Credentials Reach a Cloud Dev Service
On October 16, 2026, Nikkei Inc. disclosed its [third data breach within a month](https://www.rescana.com/post/nikkei-in
Read More