
Code Security Enhancements, Full Scan Support, Image Vulnerability Triaging, and More
Code Security Enhancements
With this release, there are major enhancements to Code Security:
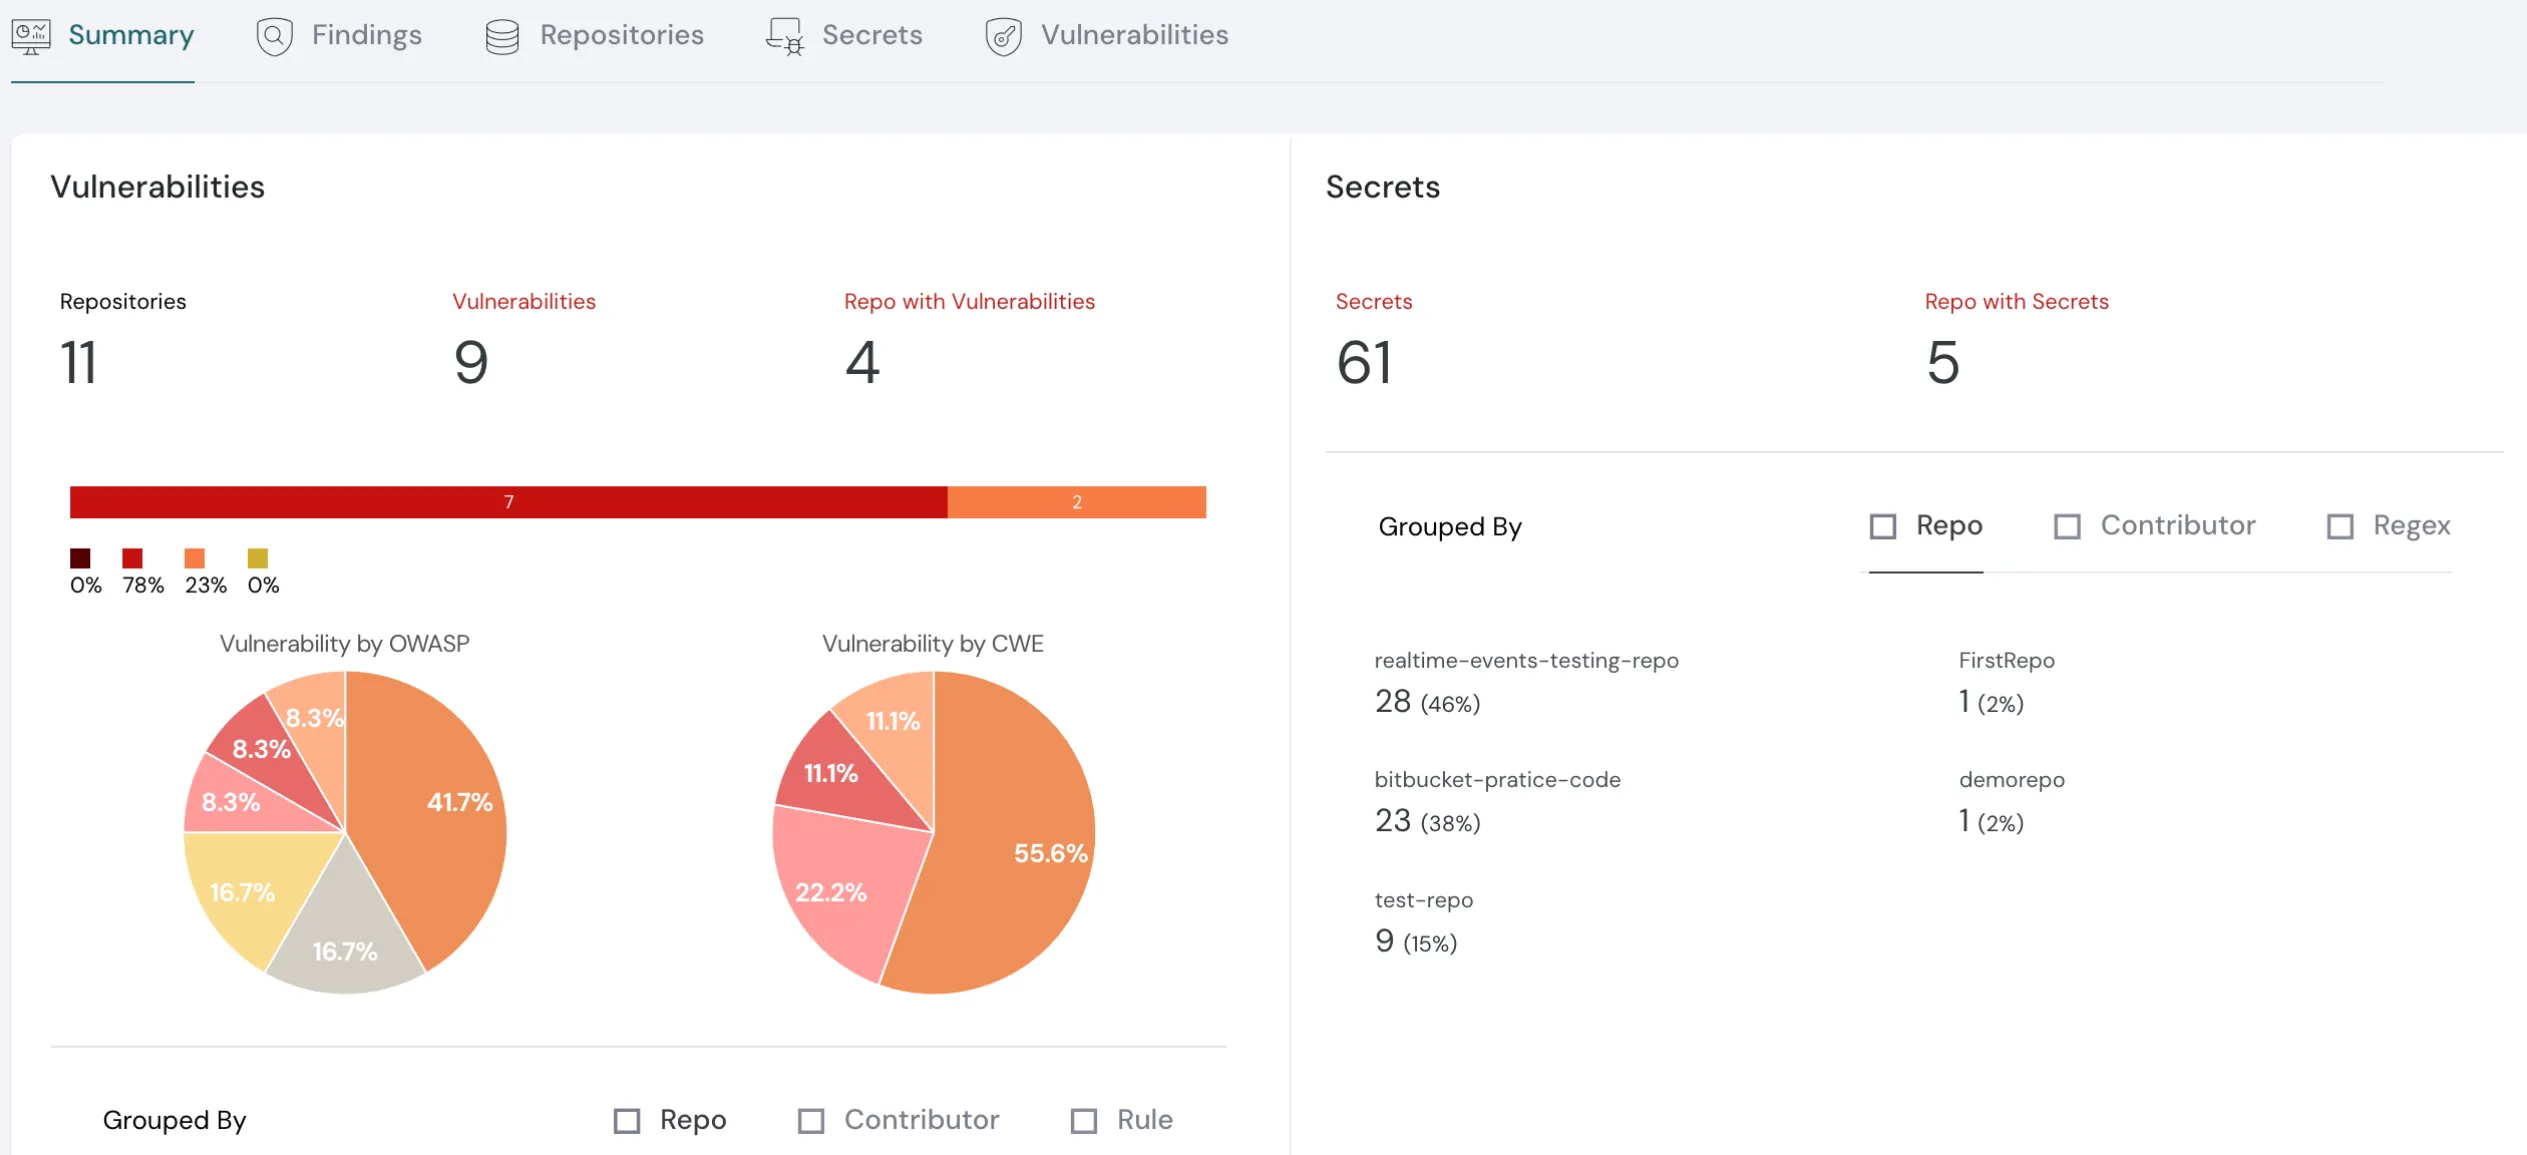
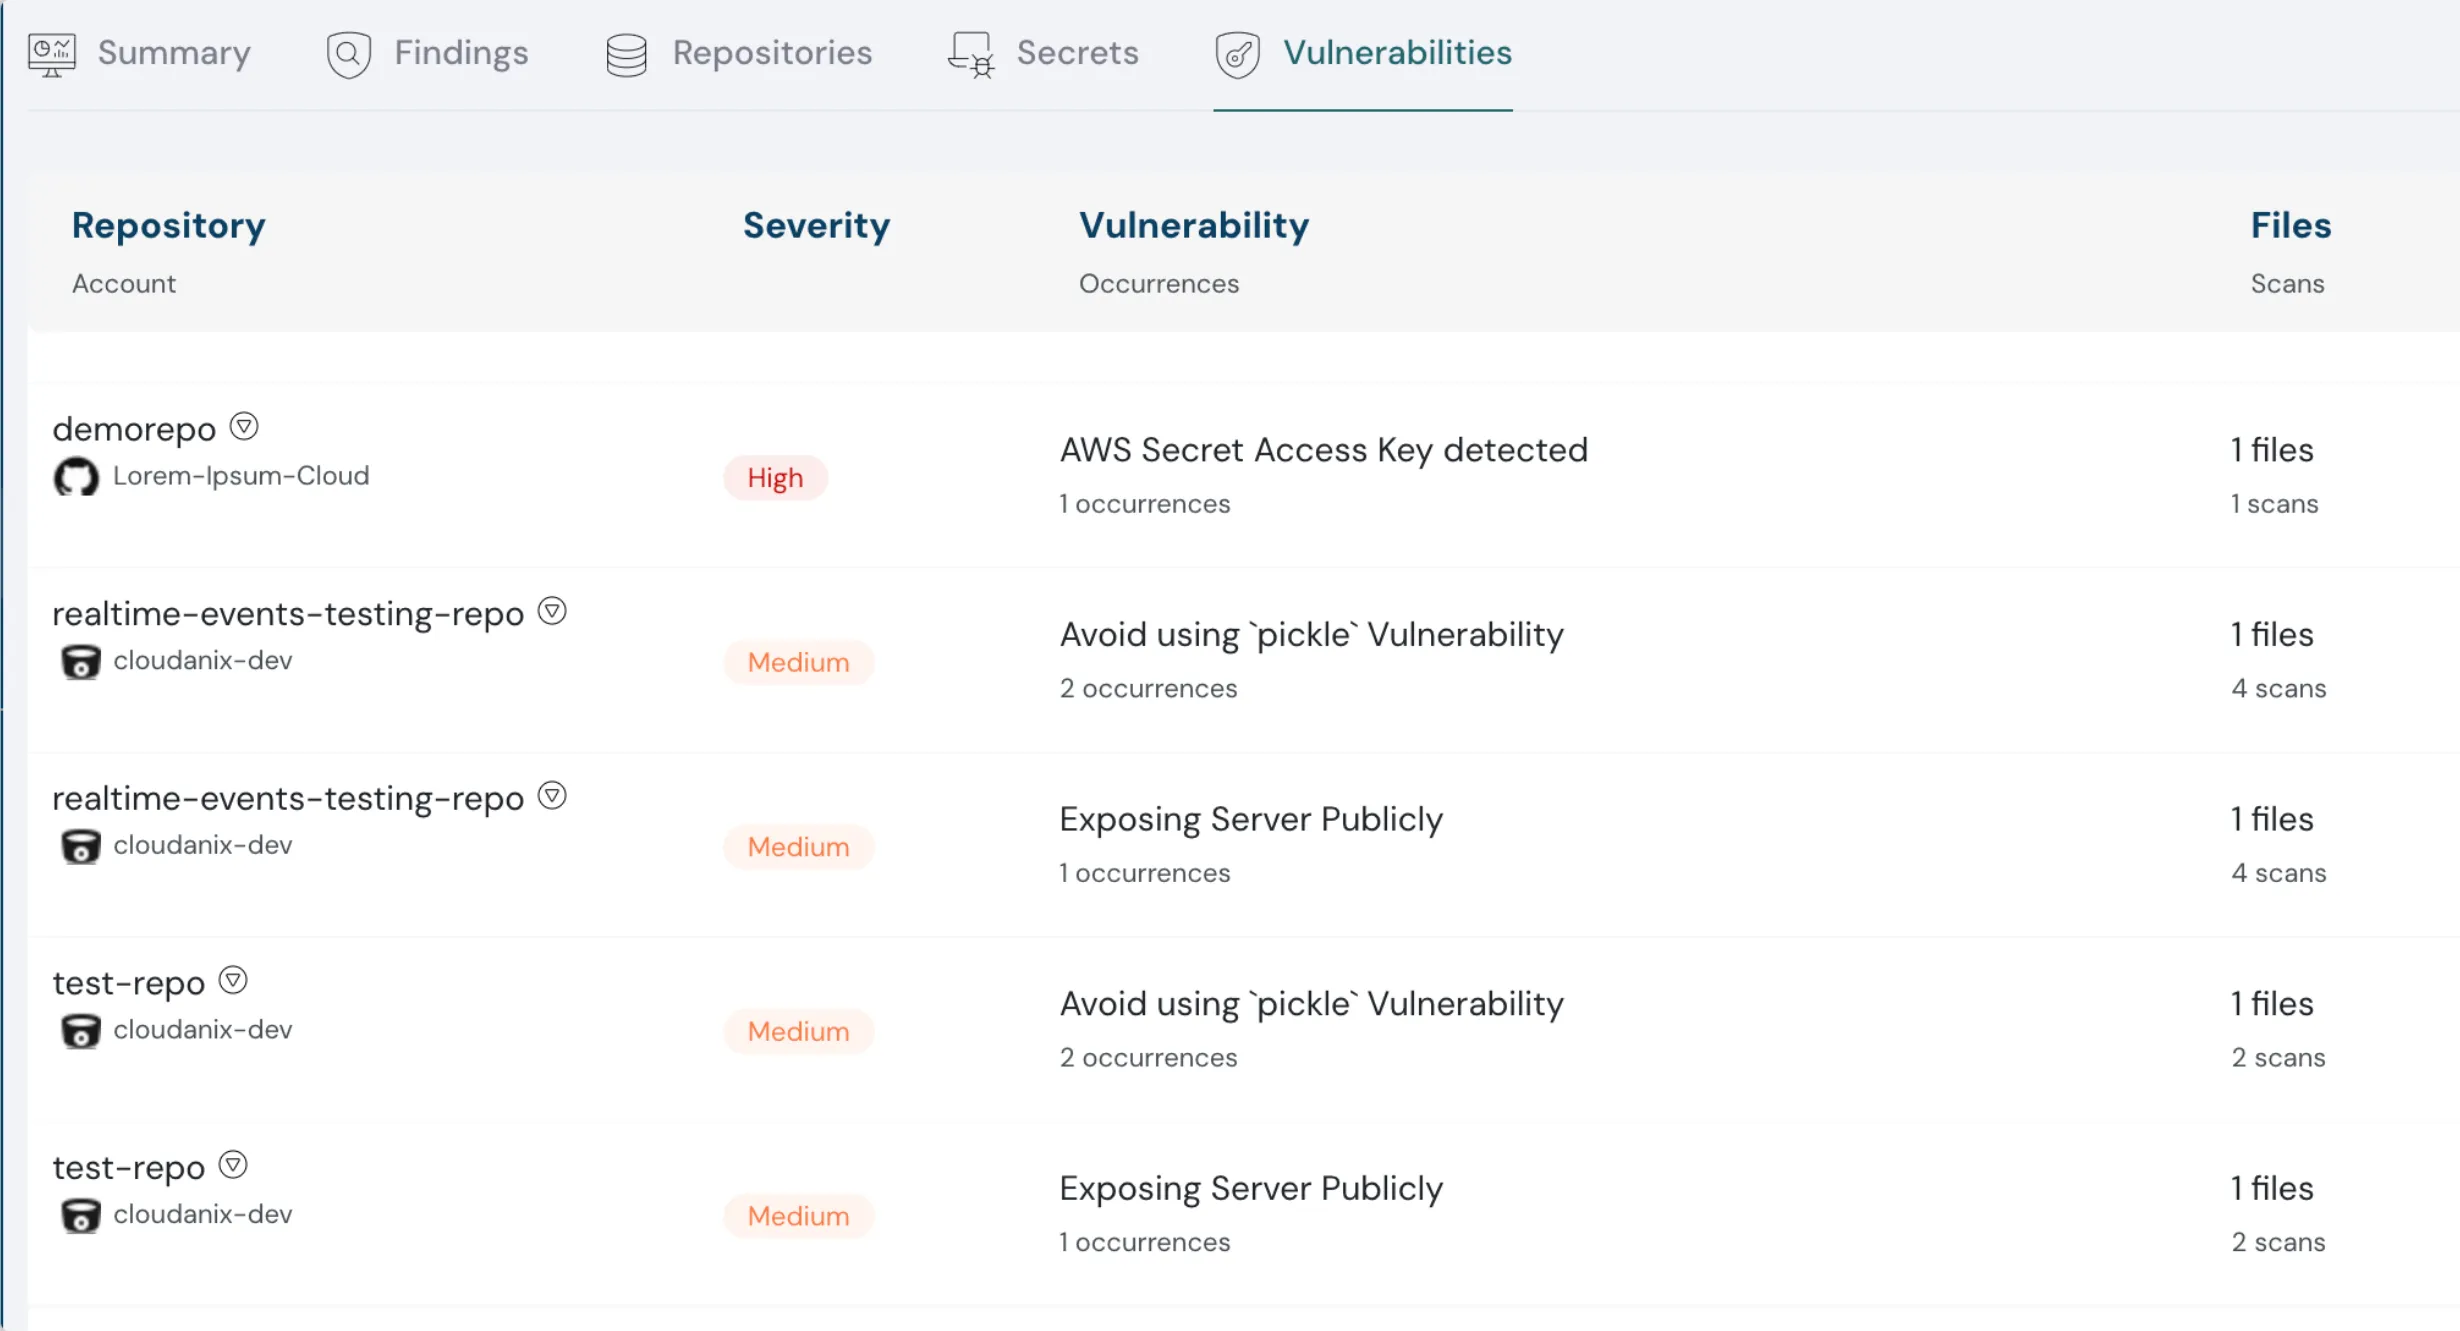
- Dedicated sections for Secrets and Vulnerabilities to dig deeper into occurrences, mapping them to files and scans.
- Improved triaging of detected secrets and vulnerabilities.
The secrets scan dashboard
List of vulnerabilities in code
Full Scan Support
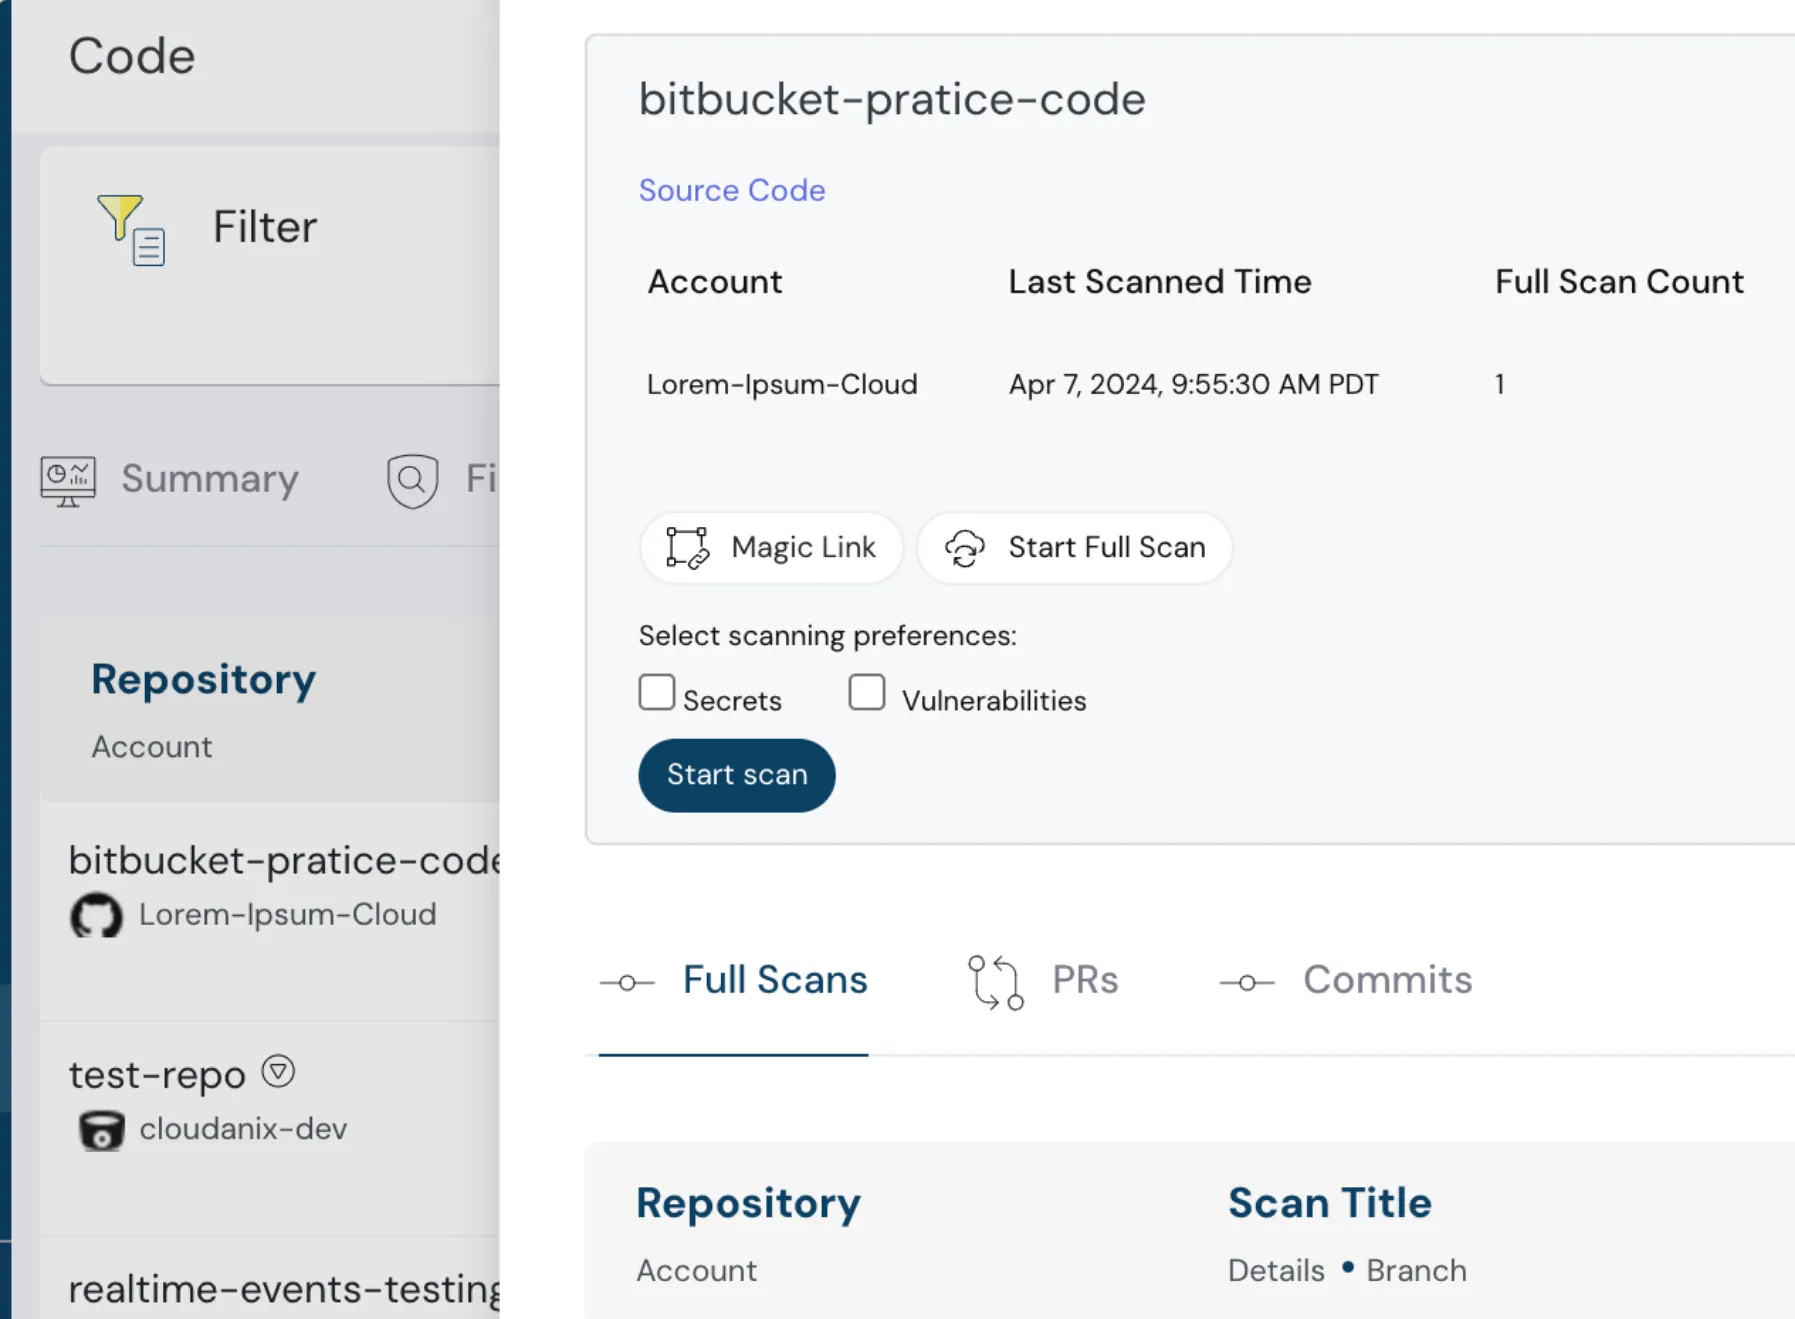
Initiate a Full Scan for GitHub or Bitbucket repositories directly from the Cloudanix Console.
This provides flexibility to start scans at will, in addition to the Weekly Automated Full Scans.
Full Scan Report for GitHub or Bitbucket
PR Check, Status, and Comments
With the latest release, customers can:
- Enforce PR Checks to fail builds based on acceptable conditions
- Add automated comments in PRs based on findings
- Insert findings status in the PRs
This reduces friction between Engineering and Security by limiting security gaps in code from reaching production.
Enforce PR Checks to fail builds based on an acceptable condition
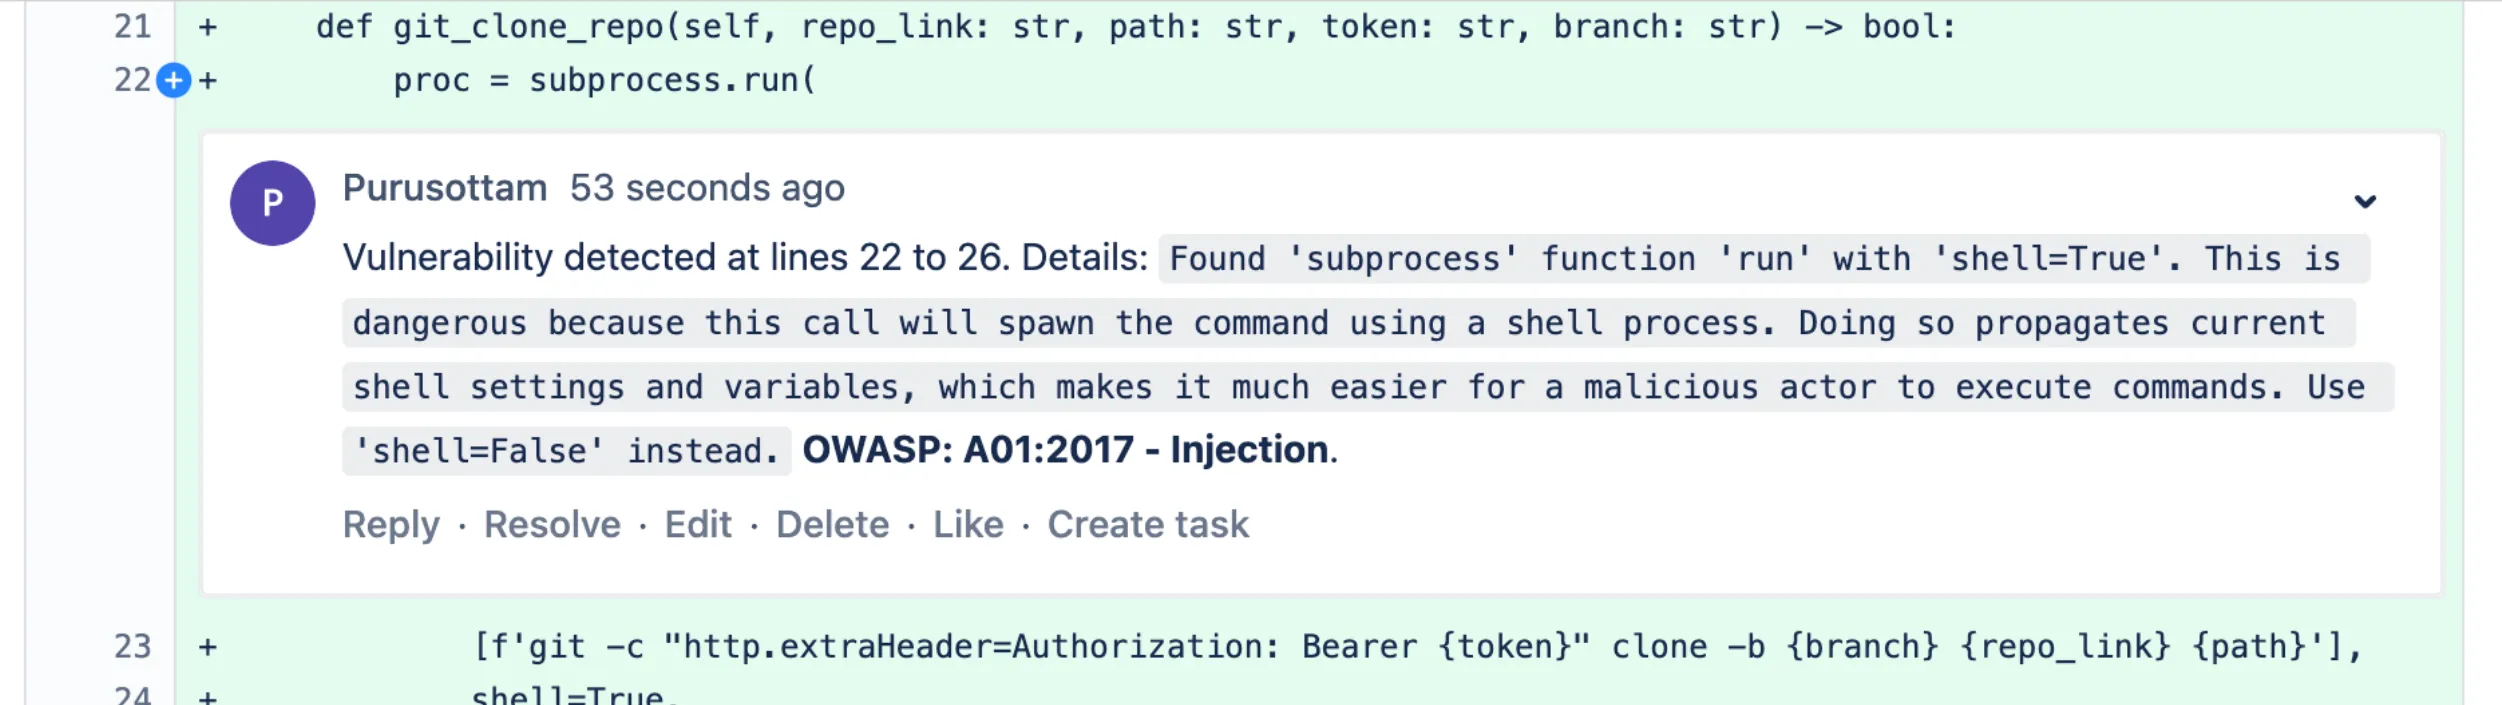
Image Vulnerability Triage
Slice and dice image vulnerability data even further using CVE or package-based filters.
Misconfiguration Policy Enhancements
We’ve expanded our AWS Misconfiguration Policy Set by another 150 policies, bringing the total to over 610. These additions provide parity with AWS Config and cover security rules across most AWS services.
Cloudanix Blogs
- Integrate IAM JIT for AWS Identity Center
- CSPM & Challenges of CSPM
- Real-Time Threat and Anomaly Detection for Workloads on AWS (co-authored with AWS)
- Announcing Cloudanix Code Security: Elevate Your Code’s Defense
Additional Resources
- Benefits of Using the Right CIEM Solution and How To Choose
- What is Code Security?
- What is Platform Engineering?
Industry News
- A Deep Dive of AWS Ransomware Attack
- Rippling’s Unique Take on Building SIEM In-House
- Declarative Images Using Code at ChainGuard
- Least Privilege and the False Sense of Security
- GitHub’s Approach to Security, Availability, and Accessibility
TODO:// is not an option for Cloud Security
Ready to see your graph?
Connect a cloud account in under 30 minutes. See every finding rooted in identity, asset, and blast radius — with a fix path attached.
Book a DemoBlog
Read More Posts
Your Trusted Partner in Data Protection with Cutting-Edge Solutions for
Comprehensive Data Security.
Wednesday, Oct 21, 2026
GhostAction: Malicious GitHub Actions Workflows Hit 30,000 Repos. Your CI/CD Is an Identity Problem
A credential-theft campaign tracked as GhostAction has been planting malicious GitHub Actions workflows into open-so
Read More
Wednesday, Oct 21, 2026
CISA Flags an Ivanti Connect Secure Zero-Day: Why the Fix Is Exposure and Blast Radius, Not Just the Patch
On October 13, 2026, CISA added a newly exploited Ivanti Connect Secure flaw — CVE-2026-104935 — to its [Known Explo
Read More
Wednesday, Oct 21, 2026
Nikkei's Third Breach in a Month: When Stolen Credentials Reach a Cloud Dev Service
On October 16, 2026, Nikkei Inc. disclosed its [third data breach within a month](https://www.rescana.com/post/nikkei-in
Read More