
BYOQ (Bring Your Own Queries), HITRUST and Much More
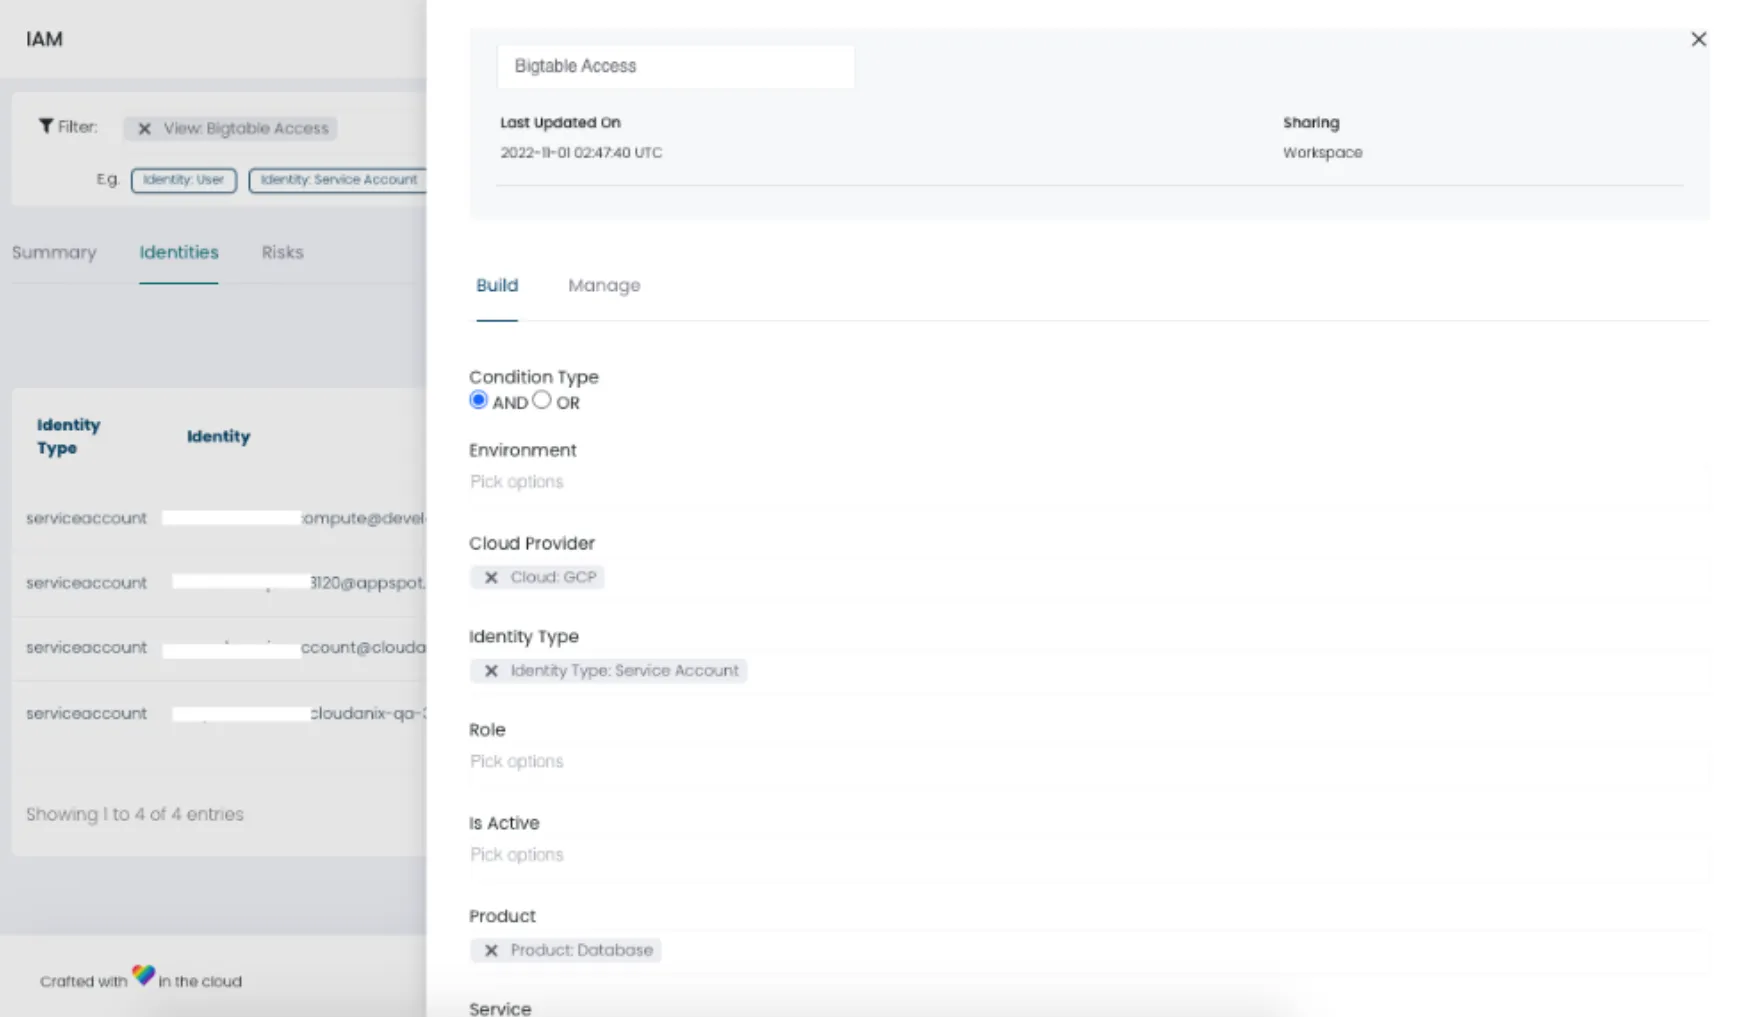
Build Your Own View
Earlier we had rolled out Inbuilt Views where we created custom views for you. But now you have the ability to Build Your Own Views.
A simple graphical interface helps you:
- Pick attributes
- Execute the query and save it
- Edit already executed queries
- Share it with your team members
Productivity and empowerment go to the next level!
Enriched IAM Screen
Your identities and their details are now presented in a tabular format. We now show you:
- Custom roles
- Granular permissions
- Various events these IAM principals have executed in your cloud accounts
Now the Principal view tells you:
- Their permissions
- Actions they have carried out
- Their review status
Announcing HITRUST and AWS Well Architected Framework Support
We have been showing your completeness against several compliance standards like HIPAA, SOC2, and many more.
Today we are rolling out two important additions:
- HITRUST
- AWS Well Architected Framework support
Setting Environments for Your Cloud Accounts
Cloudanix gives you a single dashboard for all your cloud accounts. Many customers have multiple accounts, even if they are using a single cloud provider.
Our users can now attach an environment to their cloud accounts, which can further be used in the Filter control on the page to query the information.
Ready to see your graph?
Connect a cloud account in under 30 minutes. See every finding rooted in identity, asset, and blast radius — with a fix path attached.
Book a DemoBlog
Read More Posts
Your Trusted Partner in Data Protection with Cutting-Edge Solutions for
Comprehensive Data Security.
Wednesday, Oct 21, 2026
GhostAction: Malicious GitHub Actions Workflows Hit 30,000 Repos. Your CI/CD Is an Identity Problem
A credential-theft campaign tracked as GhostAction has been planting malicious GitHub Actions workflows into open-so
Read More
Wednesday, Oct 21, 2026
CISA Flags an Ivanti Connect Secure Zero-Day: Why the Fix Is Exposure and Blast Radius, Not Just the Patch
On October 13, 2026, CISA added a newly exploited Ivanti Connect Secure flaw — CVE-2026-104935 — to its [Known Explo
Read More
Wednesday, Oct 21, 2026
Nikkei's Third Breach in a Month: When Stolen Credentials Reach a Cloud Dev Service
On October 16, 2026, Nikkei Inc. disclosed its [third data breach within a month](https://www.rescana.com/post/nikkei-in
Read More